An IAM role created by our CloudFormation template, with ExternalId, is enough to inventory an account; the accounts of an organisation are discovered and added in bulk.
EC2, EBS and snapshots, S3, IAM (users, groups, roles, policies, credential report), RDS and clusters, EKS, ECS, ECR, Lambda and its layers, CloudTrail, CloudWatch, KMS, Secrets Manager, GuardDuty, Security Hub, WAF, Shield, CloudFront, API Gateway, SageMaker, Bedrock, DynamoDB, OpenSearch, Glue, EMR, Athena, Cognito, Backup, Route 53, VPC and peerings.
What you get
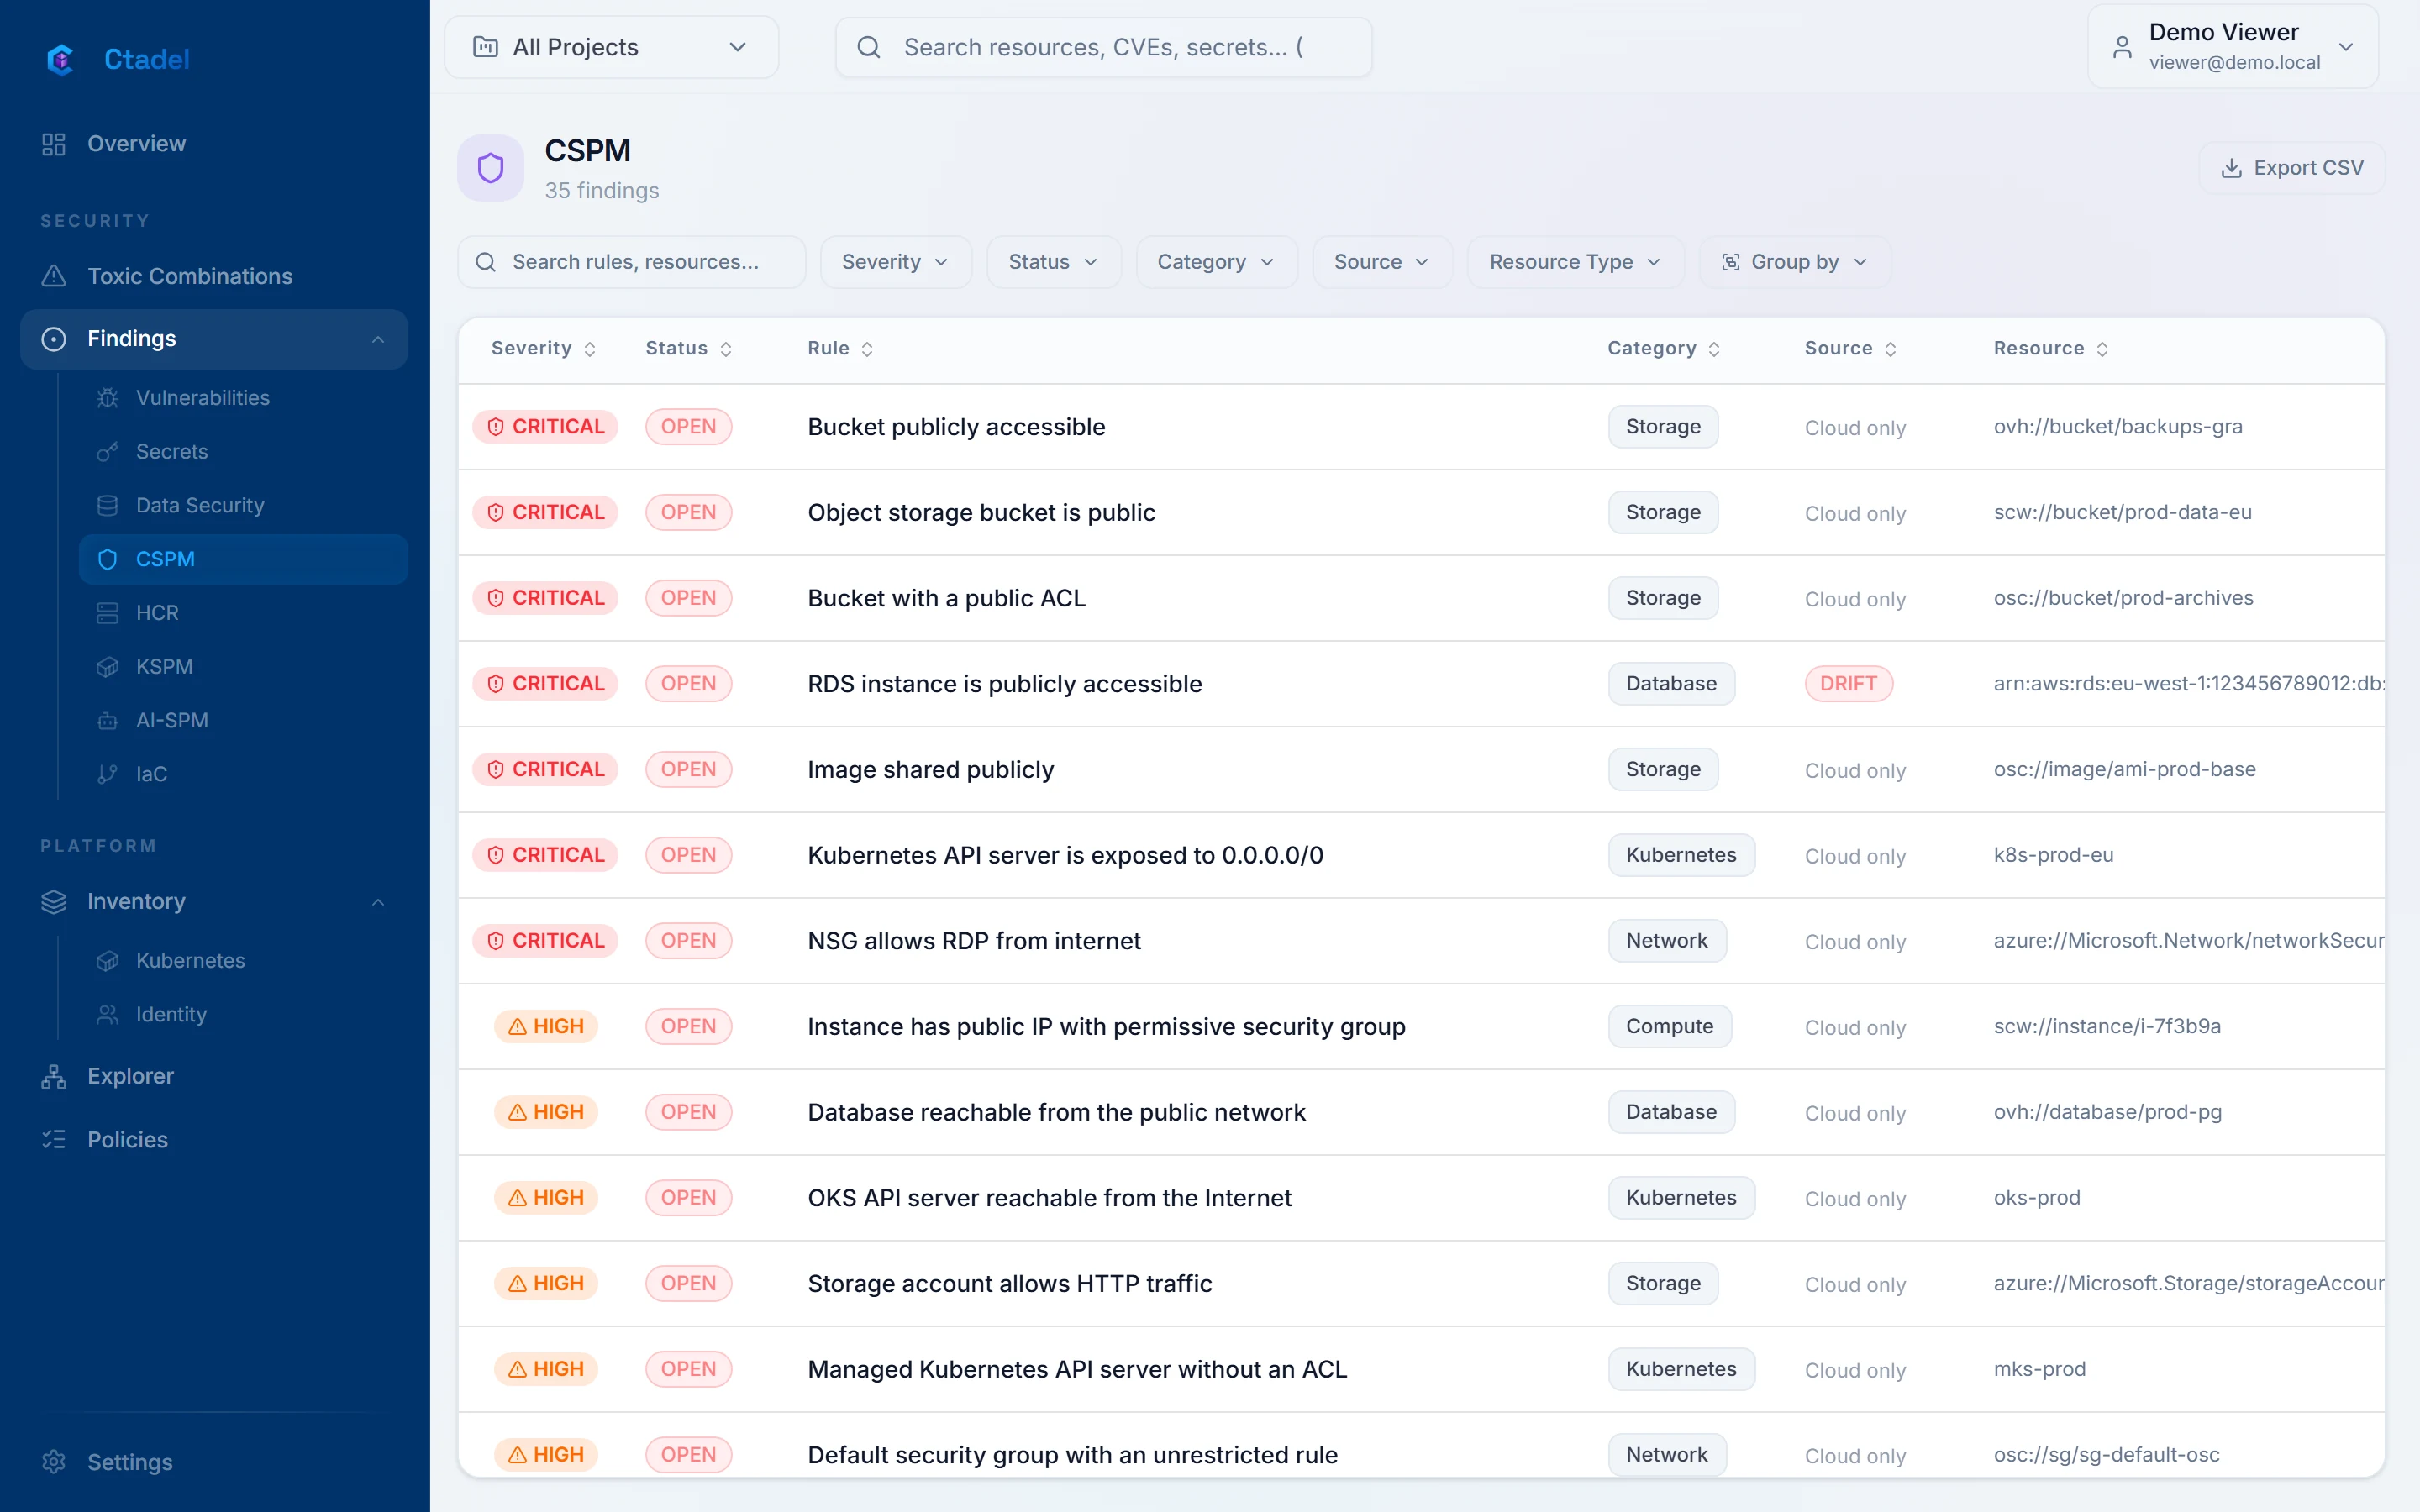
The posture of each account, effective permissions computed from IAM policies and assumable roles, sensitive data in S3 and RDS databases, valid secrets, instance and image vulnerabilities, managed AI services (Bedrock, SageMaker) and toxic combinations, for instance a public instance assuming a role that reads a database holding personal data.
Assumable roles and privilege escalations in the graph
Snapshots shared with other accounts detected
AWS Terraform analysed on every pull request, with drift between code and what is deployed
The access requested
An IAM role created by the CloudFormation template, with the managed policies SecurityAudit and ViewOnlyAccess, an ExternalId and an adjustable session duration. The template options separately enable disk copy, database copy, bucket content reading and EKS cluster access; each can be disabled.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.