
Secrets
The keys lying around, and whether they still work
Provider patterns on buckets, disks, function variables and Git repositories. When the service allows it, validity is checked with a harmless read call: a valid key in a public bucket is not a finding like the others.
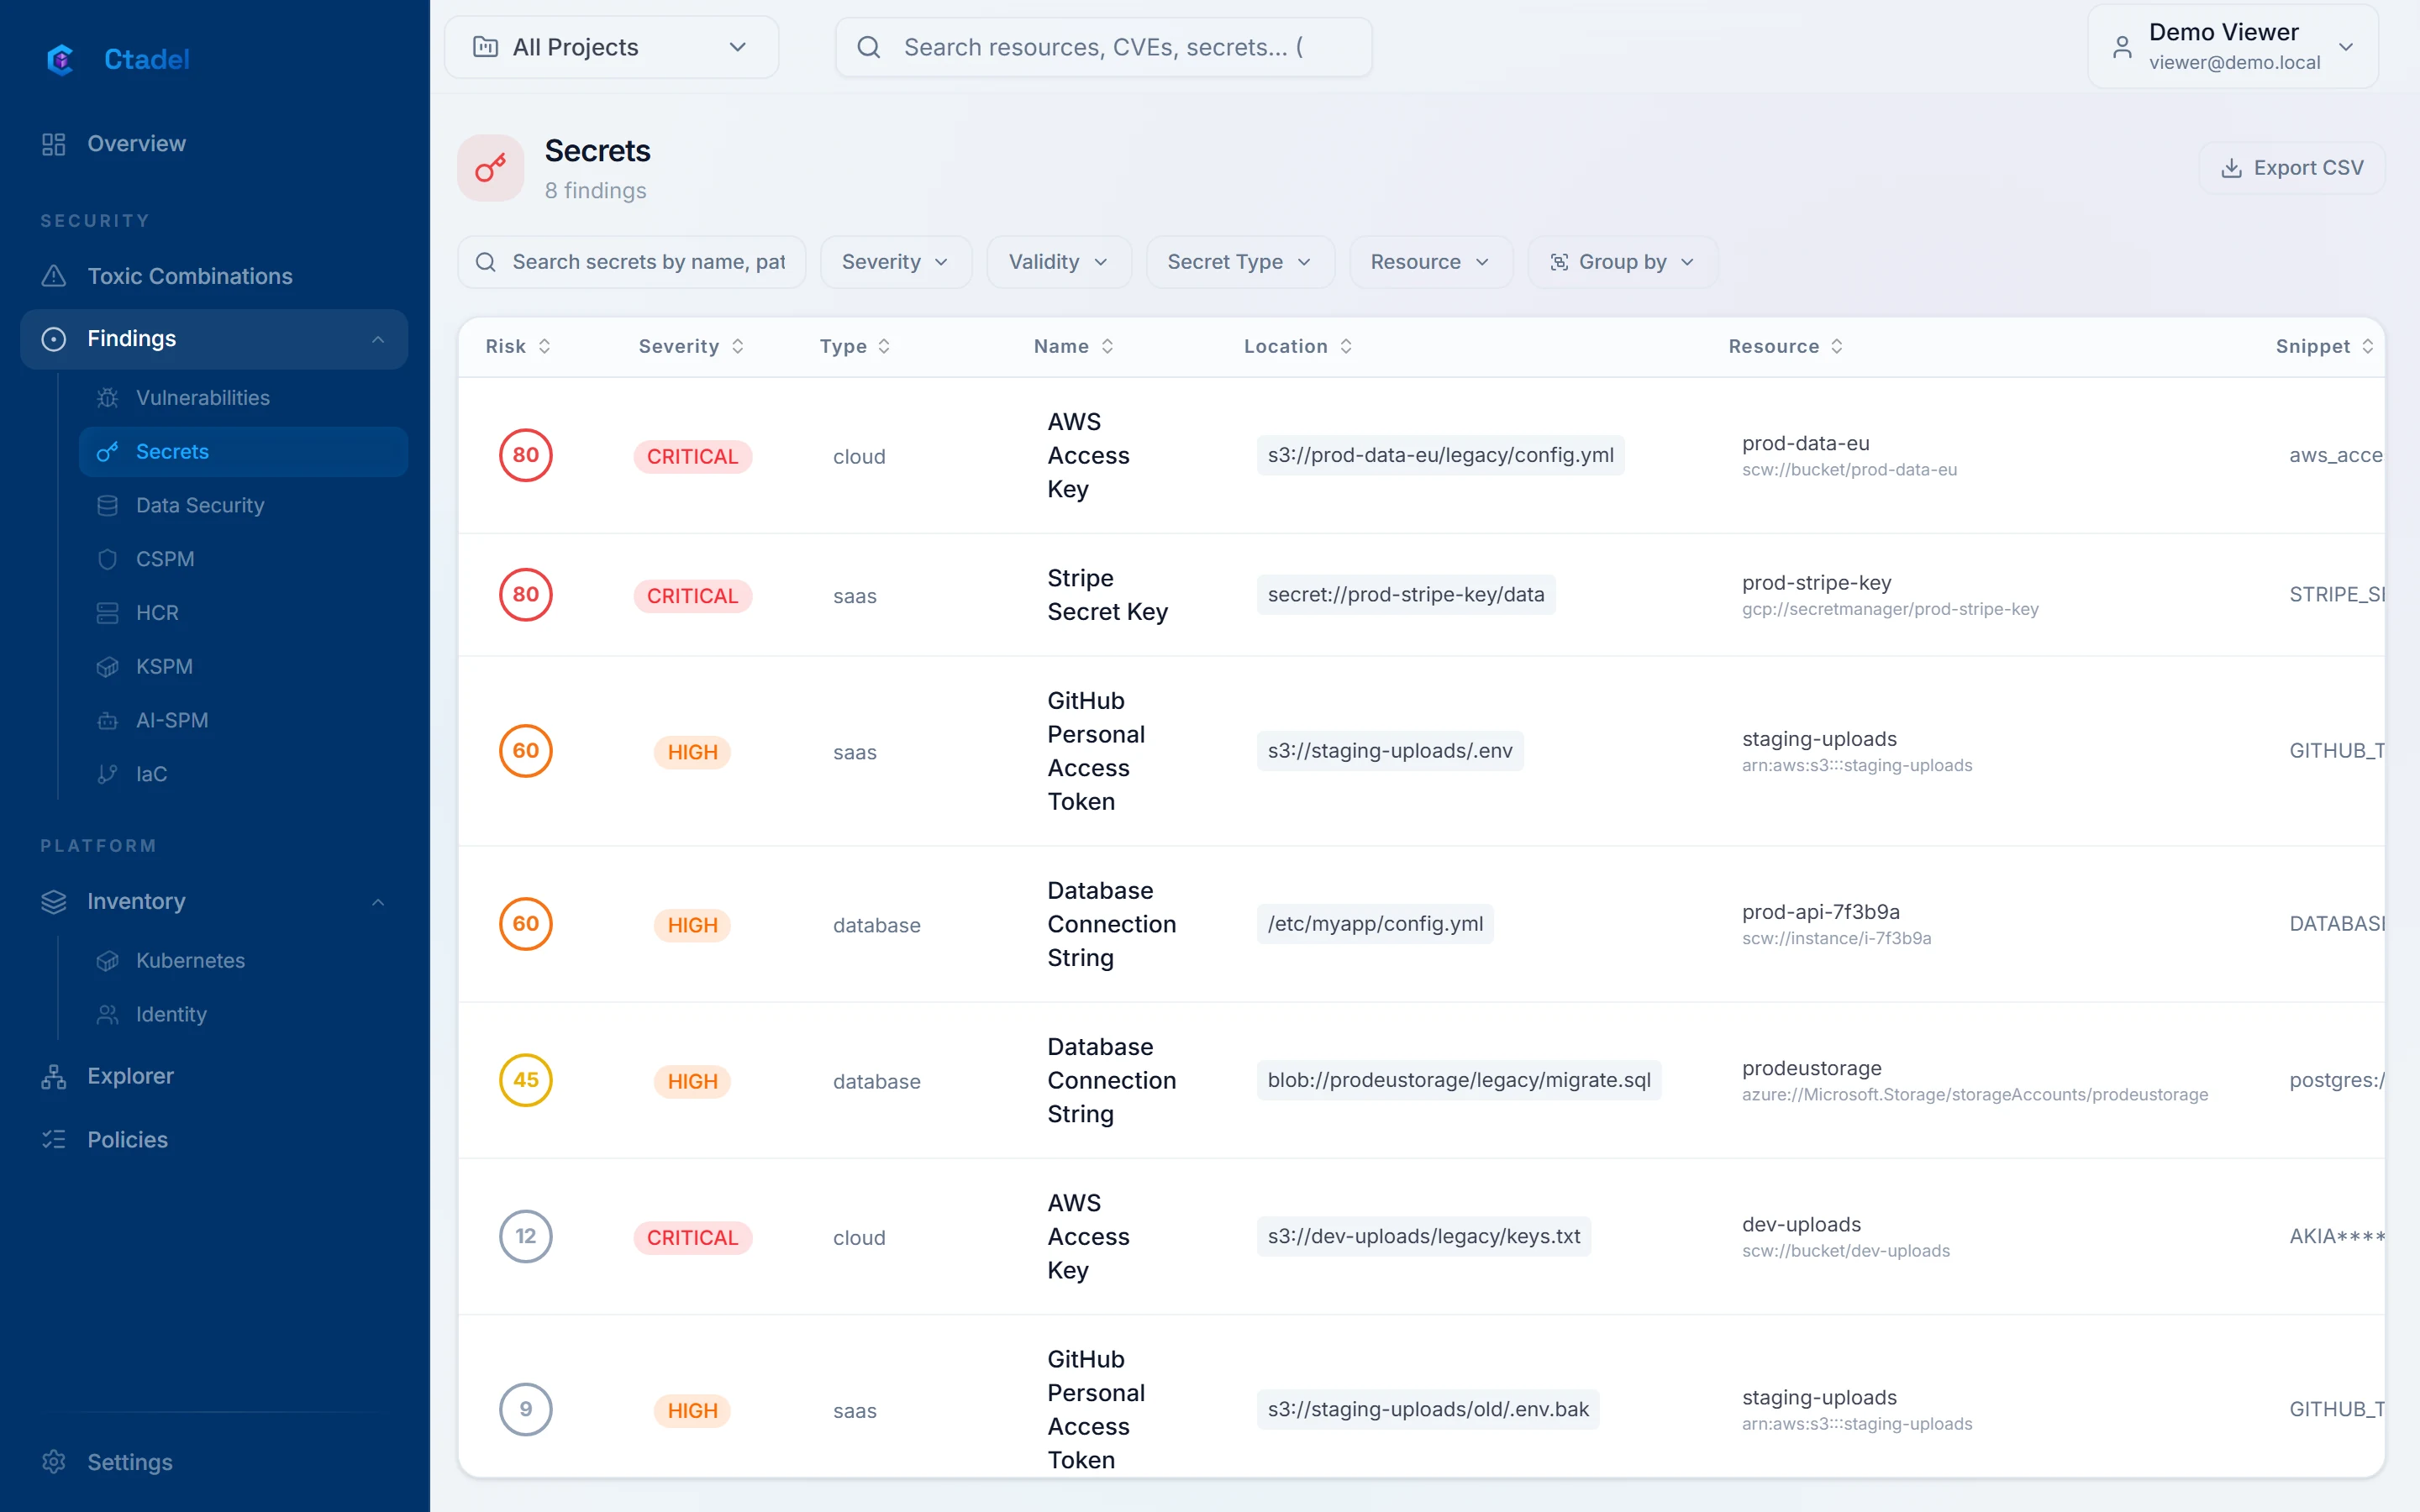
- What is read
- API keys, tokens, passwords and private keys in buckets, disks, functions and repositories.
- How
- Patterns per provider; validity checked with a harmless read call when the service allows it.
- In the application
- Secrets page: masked value, location, validity active, revoked or unknown.
What it cannot see. Validity checks only exist for services that expose a harmless read call. Other secrets keep the unknown status.
Example detections
- Valid AWS access key in a public bucket
- GitHub token in a function variable
- SSH private key reused between staging and production
The other modules
Ready to see this module on your accounts?
The public demonstration runs on fictitious data. For an instance on your own accounts, request a demonstration.