
CIEM
Effective permissions, not declared ones
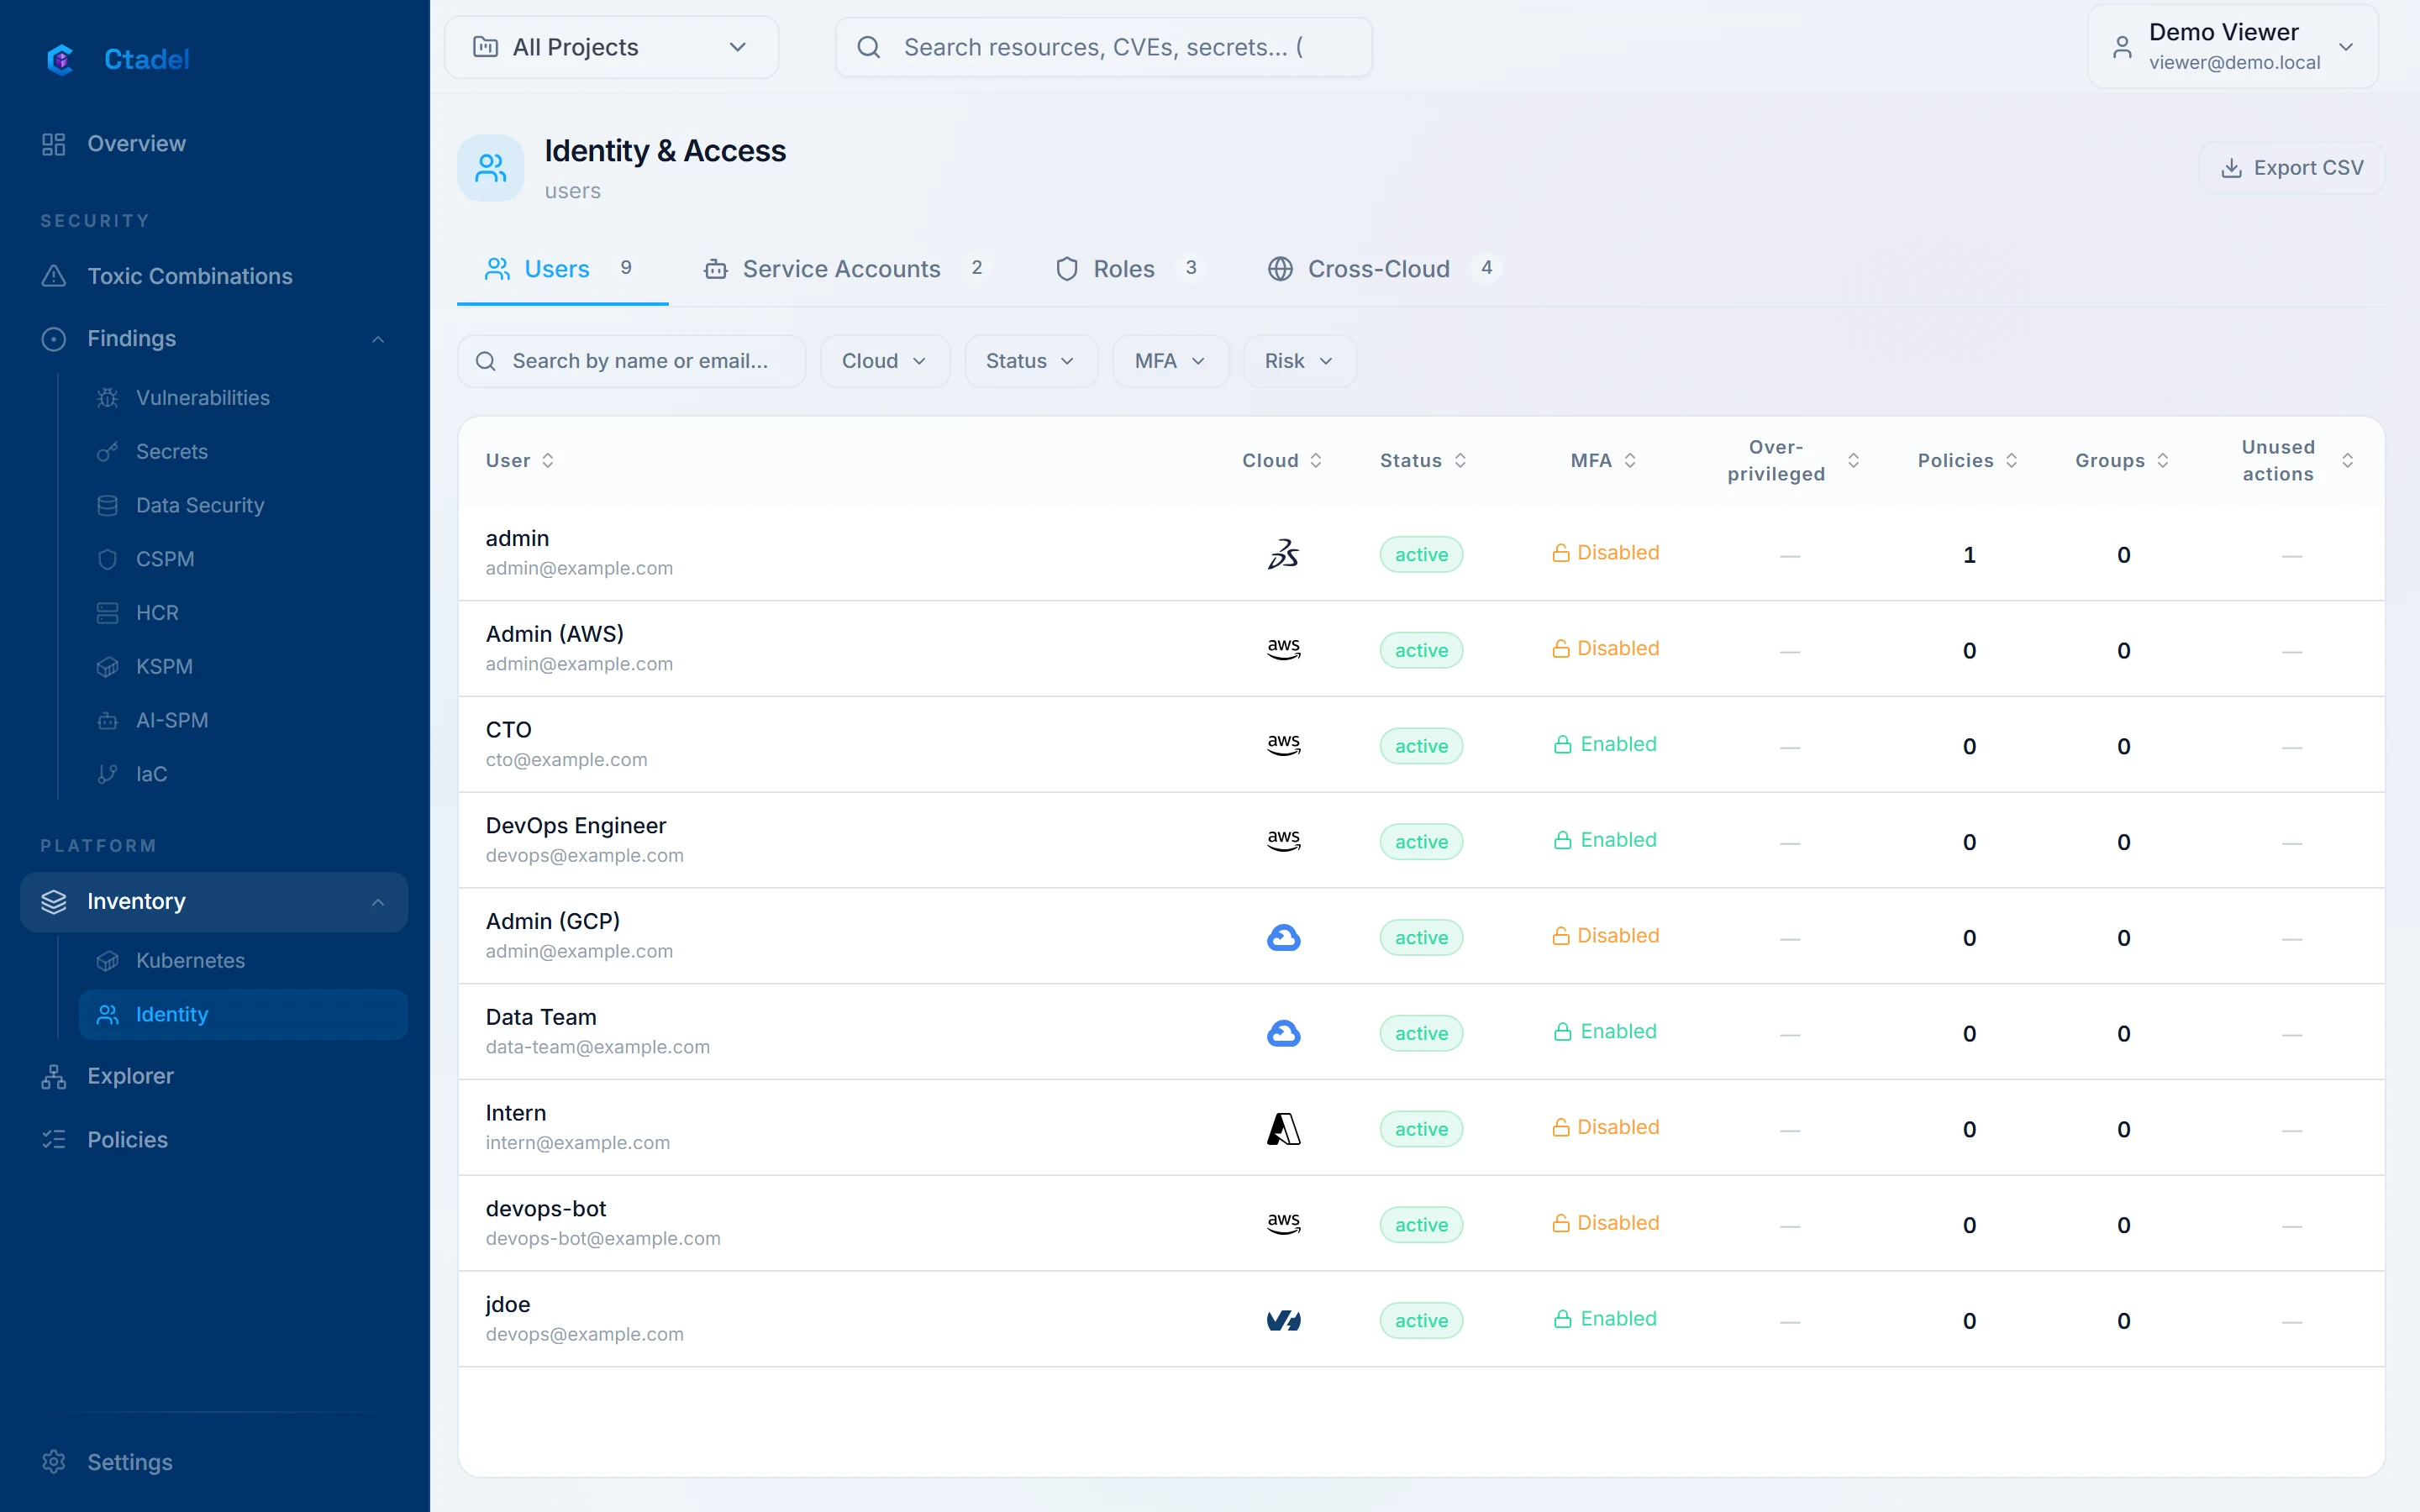
Users, groups, roles, service accounts and policies of the six clouds, with what they can really do, what they never use, and the identities that exist on several clouds at once.
- What is read
- Users, groups, roles, service accounts, policies and assignments across the six clouds.
- How
- Effective permissions computed in the graph according to each cloud’s model, unused permissions, identities shared across clouds.
- In the application
- Identity page: effective permissions, unused permissions, least-privilege recommendations, administrator accounts, cross-cloud matches.
What it cannot see. Least-privilege recommendations depend on the usage history the cloud exposes; without history, only the extent of the permissions is evaluated.
Example detections
- Administrator identity present on several clouds without a second factor
- Role that allows escalating to administrator
- Access key never used since its creation
The other modules
Ready to see this module on your accounts?
The public demonstration runs on fictitious data. For an instance on your own accounts, request a demonstration.