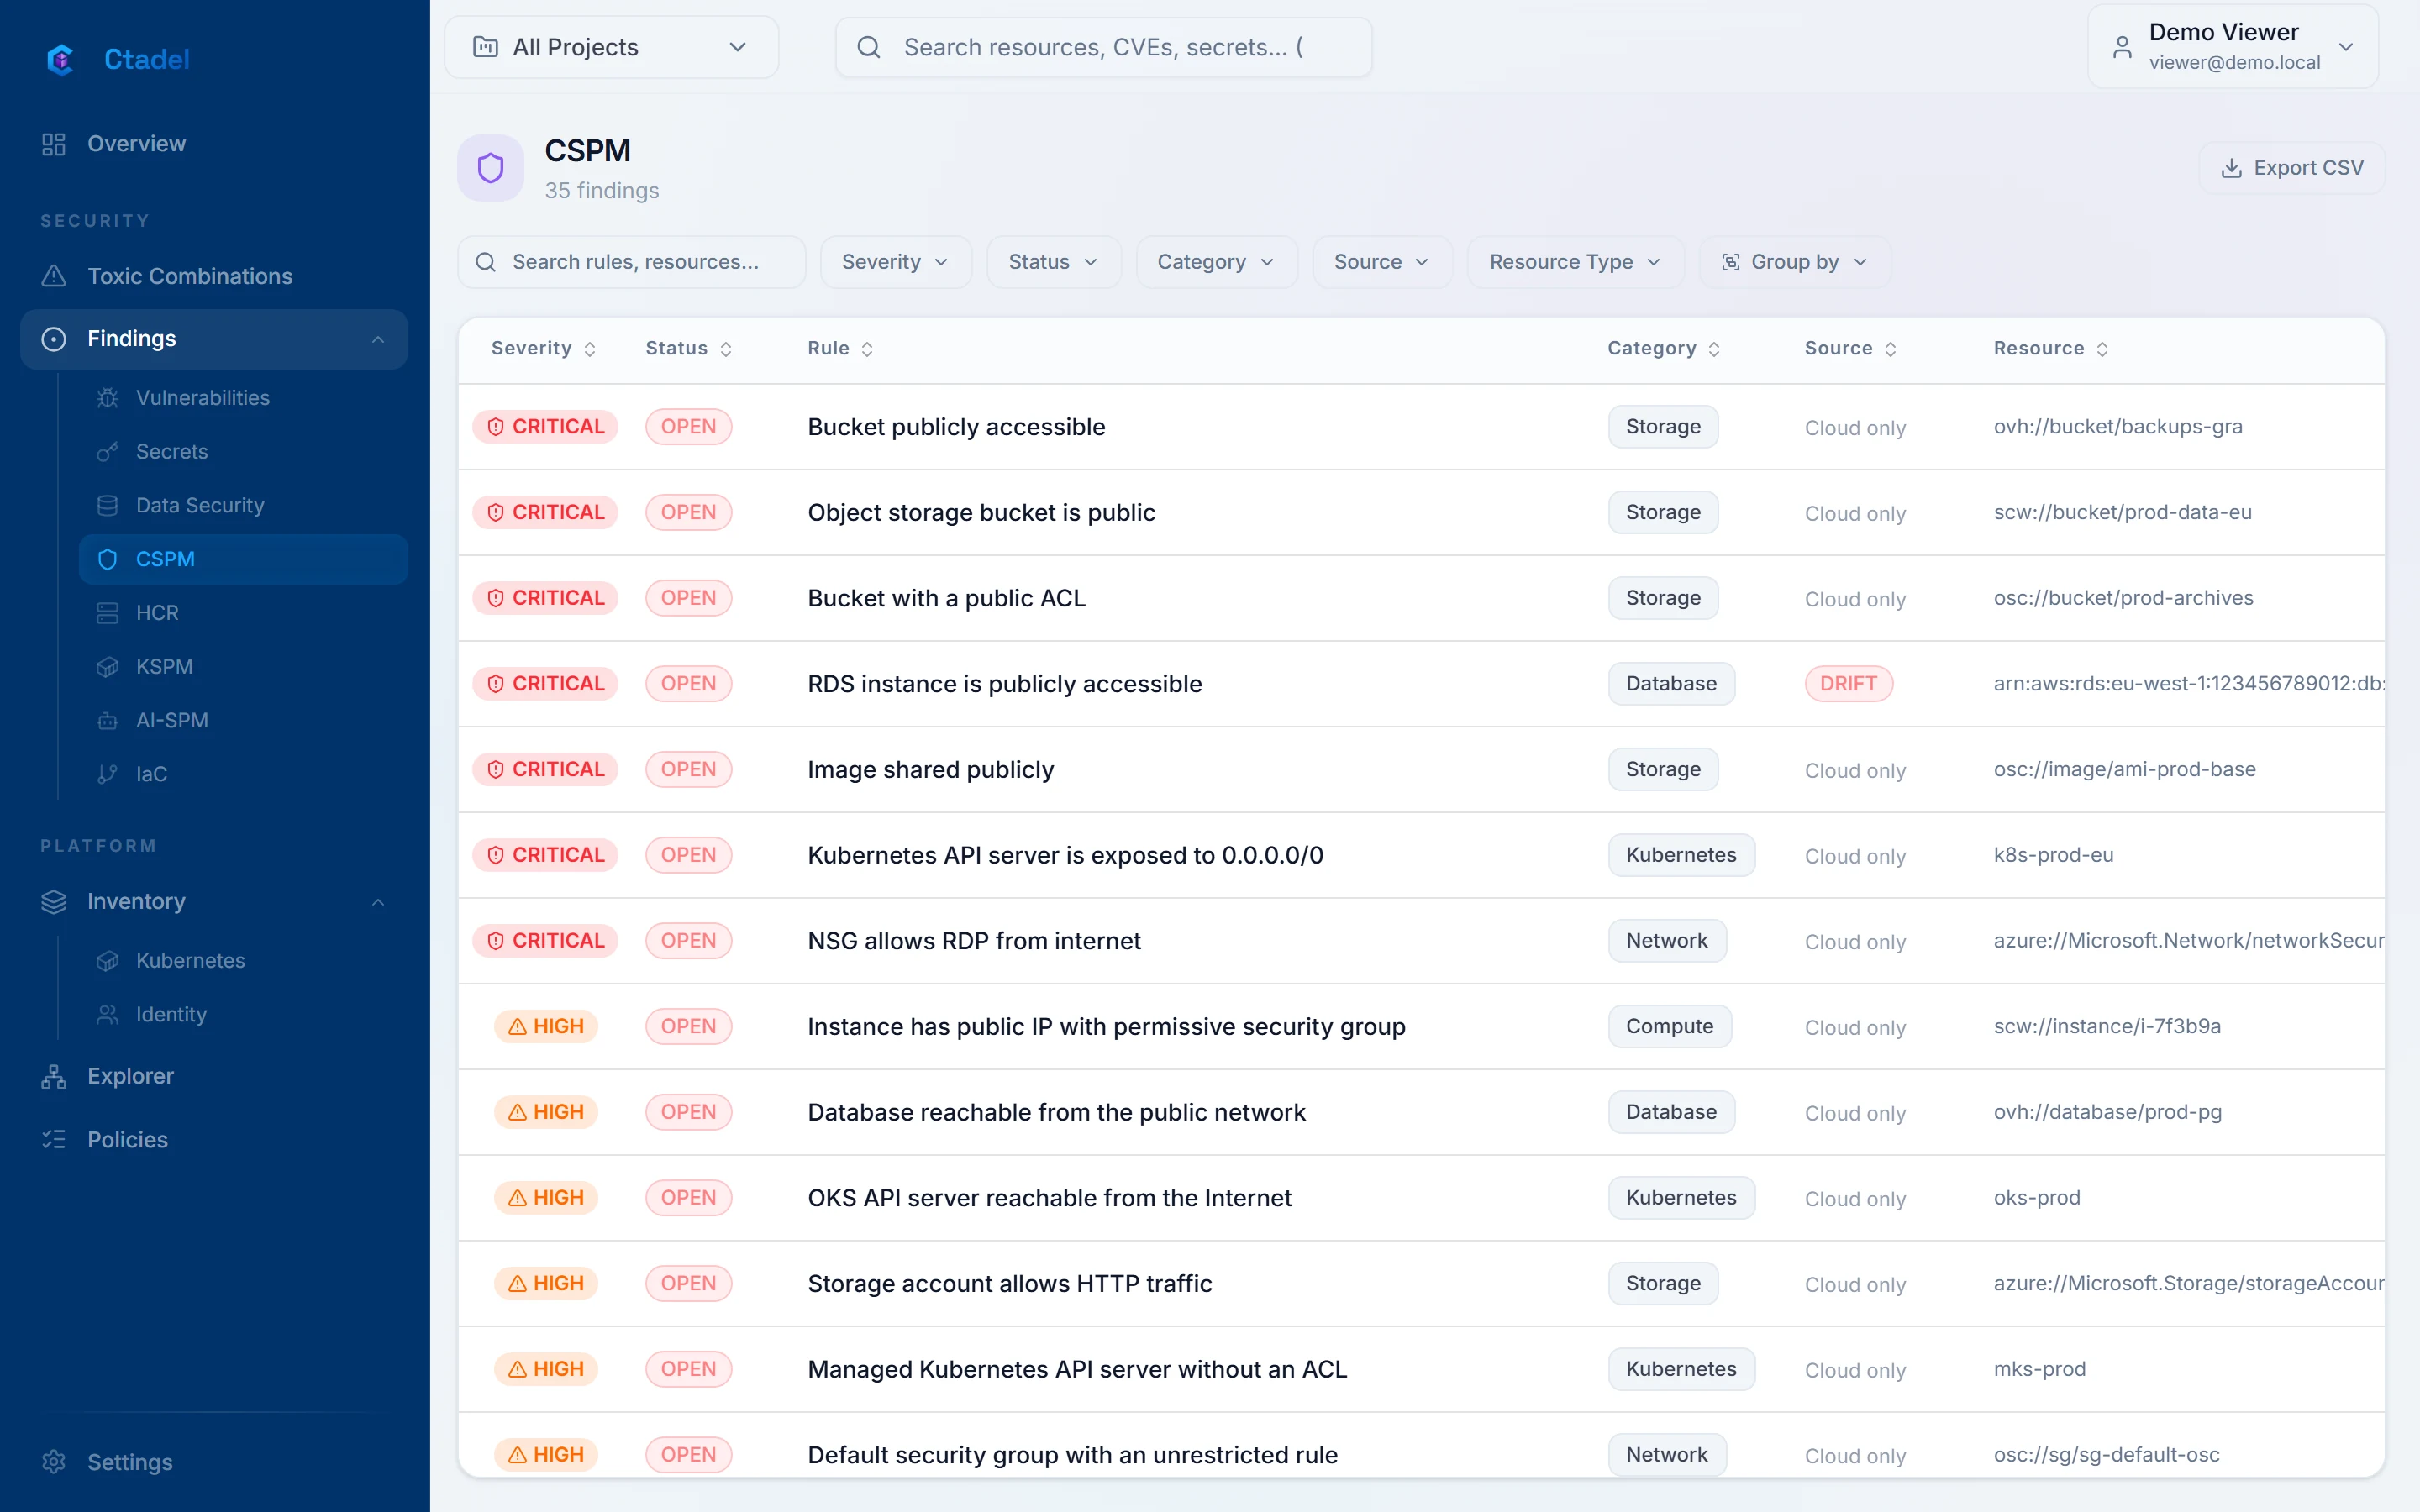
The posture of each project, effective permissions of service accounts and members, sensitive data in Cloud Storage and Cloud SQL, secrets, instance vulnerabilities, Vertex AI Workbench instances, and toxic combinations.
Public buckets, service accounts with keys, open firewall rules
GKE read through the cluster API
google Terraform analysed on every pull request
The access requested
A service account key, or keyless identity federation (external_account). Disk and database analysis requires additional copy permissions in the project.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.