Security for your Scaleway projects, at the same level as AWS
Ctadel reads your Scaleway organisation through the API, with an IAM application key, and applies to Scaleway the same scanners and attack paths as to the hyperscalers.
Instances, Elastic Metal, volumes and snapshots, Object Storage buckets, managed databases, Kapsule, serverless containers and functions, IAM (applications, policies, keys), Key Manager, Secret Manager, load balancers, VPC and gateways, security groups, flexible IPs, domains, container registry.
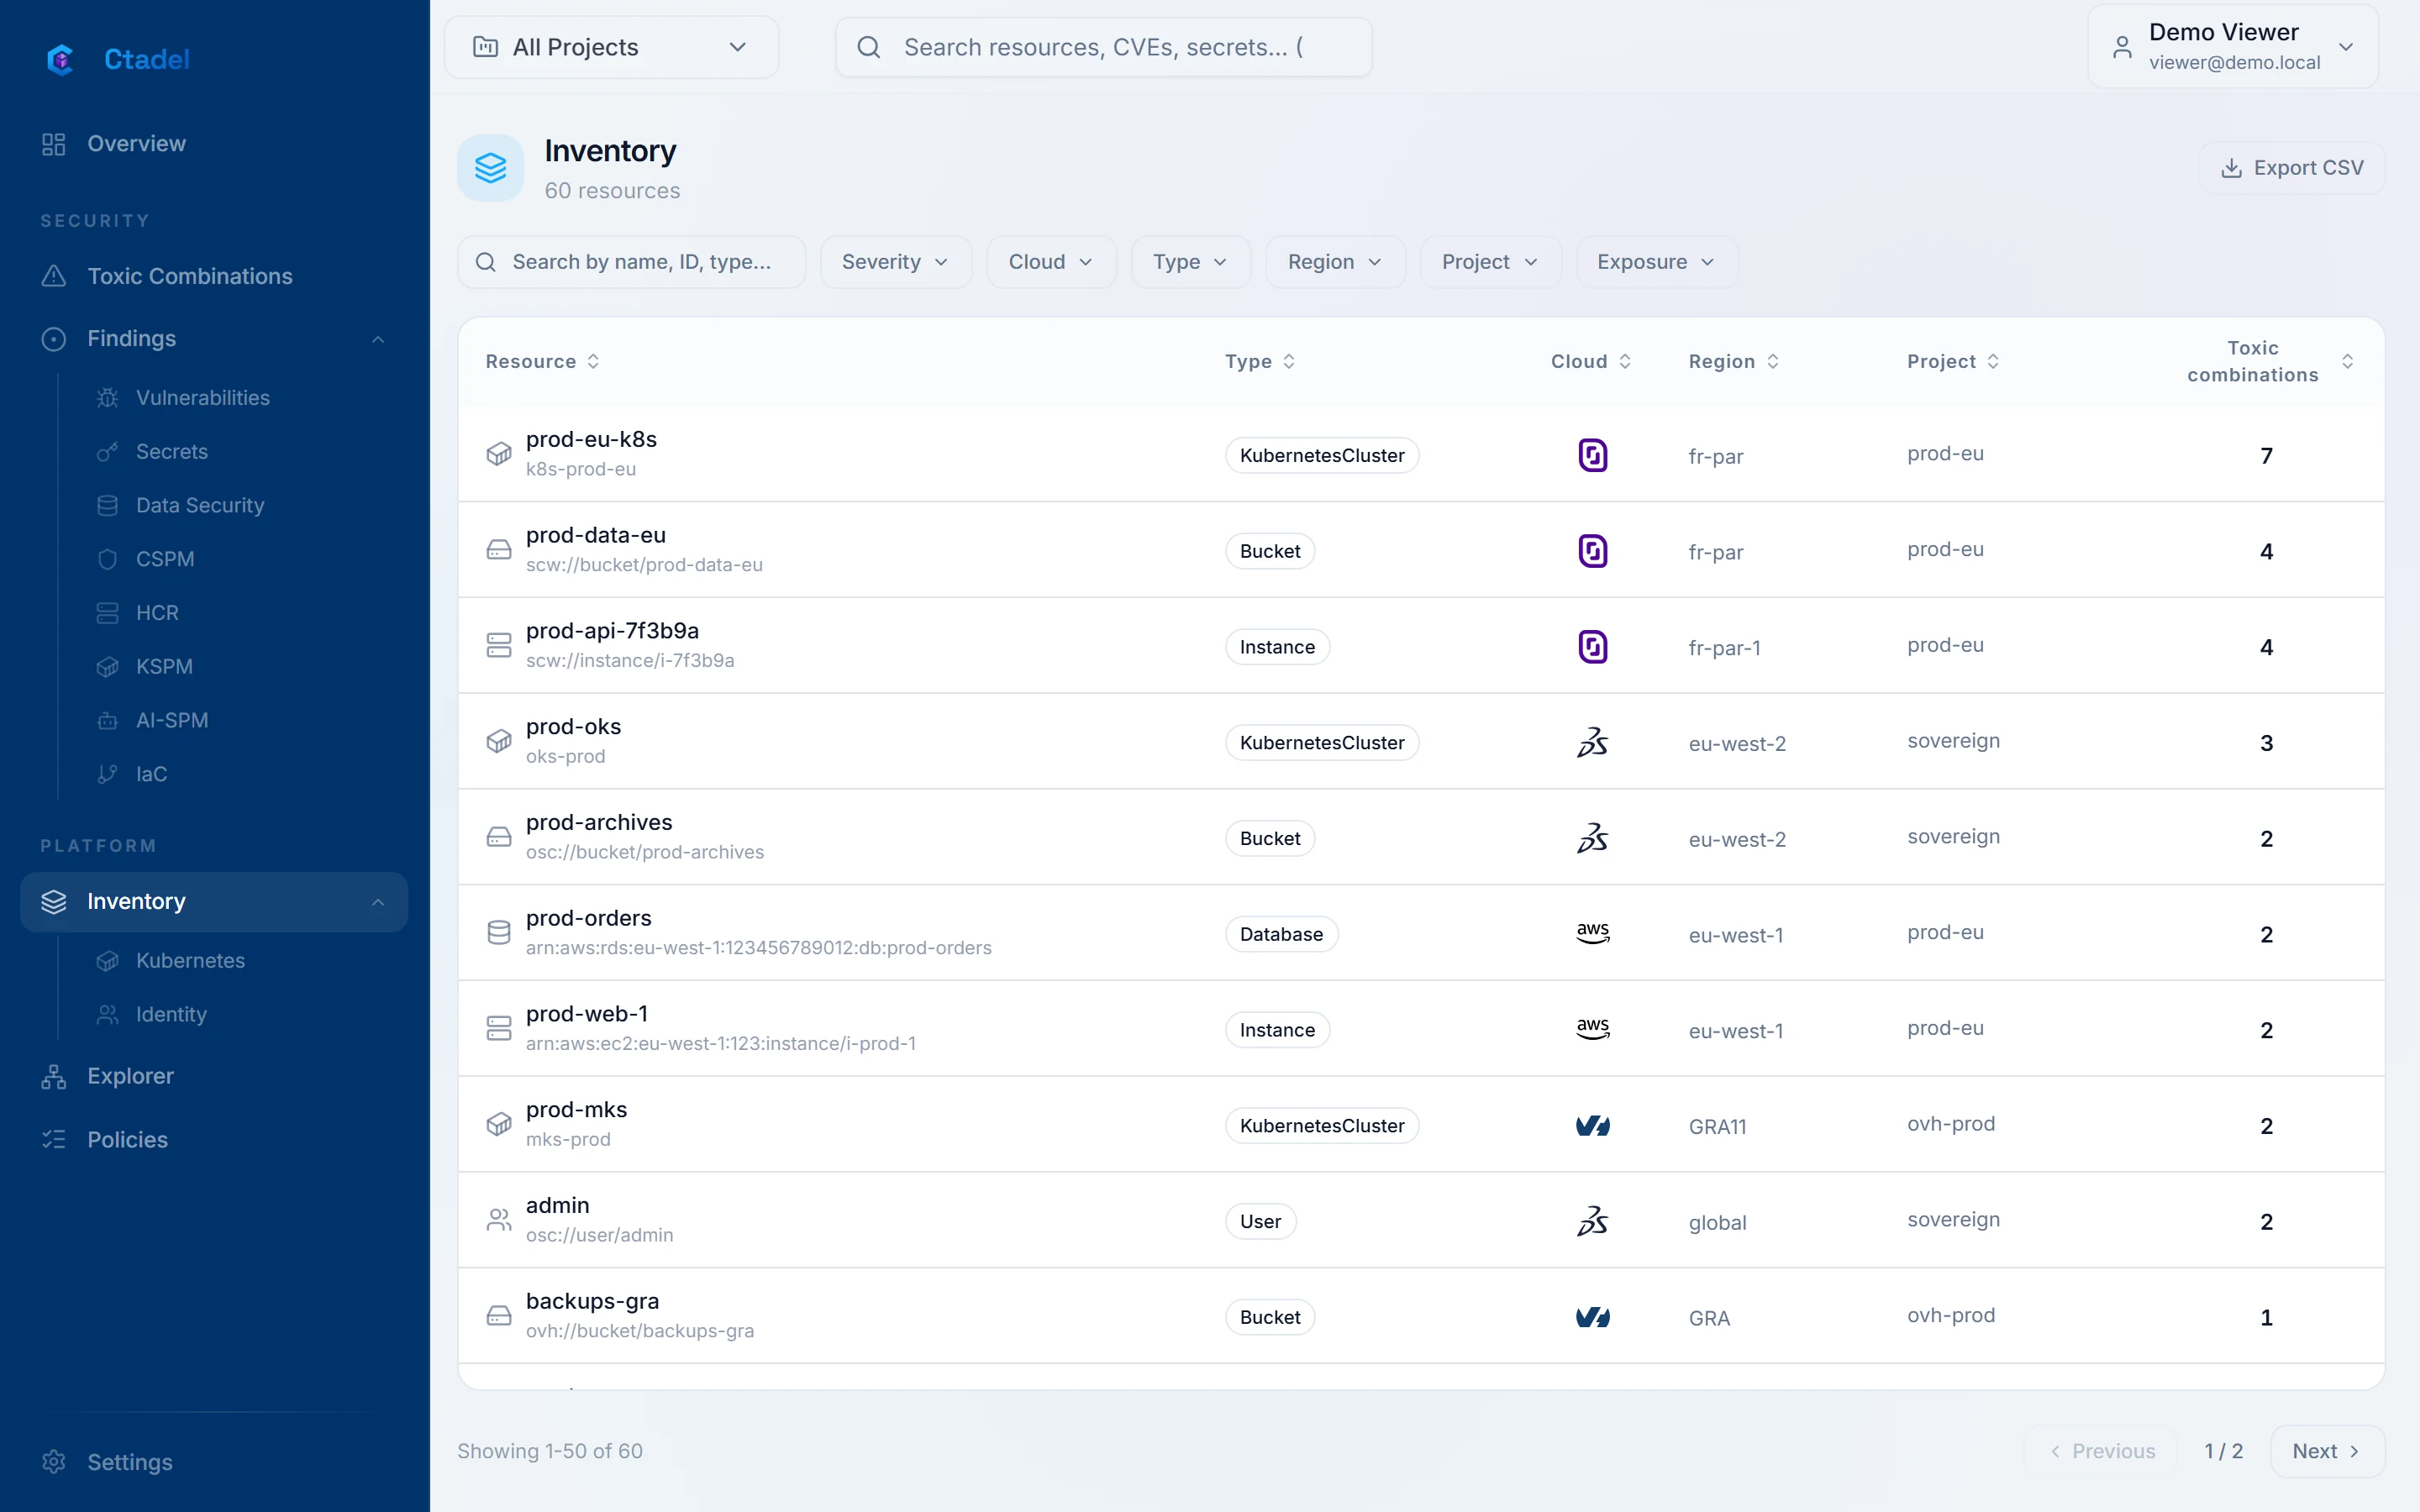
Every resource enters the graph with its relationships: a bucket belongs to a project, an instance carries a security group, an API key belongs to an application. Configuration rules are queries on that graph.
What you get
Configuration findings (public bucket, security group open to all, database reachable from the internet, never-used API key), effective permissions of IAM applications, sensitive data found in buckets, still-valid secrets, instance vulnerabilities and the toxic combinations connecting them.
Kapsule read through the cluster API, workloads and RBAC included
Disk analysis on an ephemeral copy inside your project
Scaleway provider Terraform analysed on every pull request
The access requested
An API key of a dedicated IAM application, with the read policies AllProductsReadOnly, IAMReadOnly and OrganizationReadOnly. Disk and database analysis additionally requires permissions to create and delete snapshots and instances, which you may decline.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.