
DSPM
What your buckets and databases really contain
Objects are sampled, databases read on a temporary copy inside your account, destroyed afterwards. Only masked excerpts are kept, and every piece of data found joins the graph for attack paths.
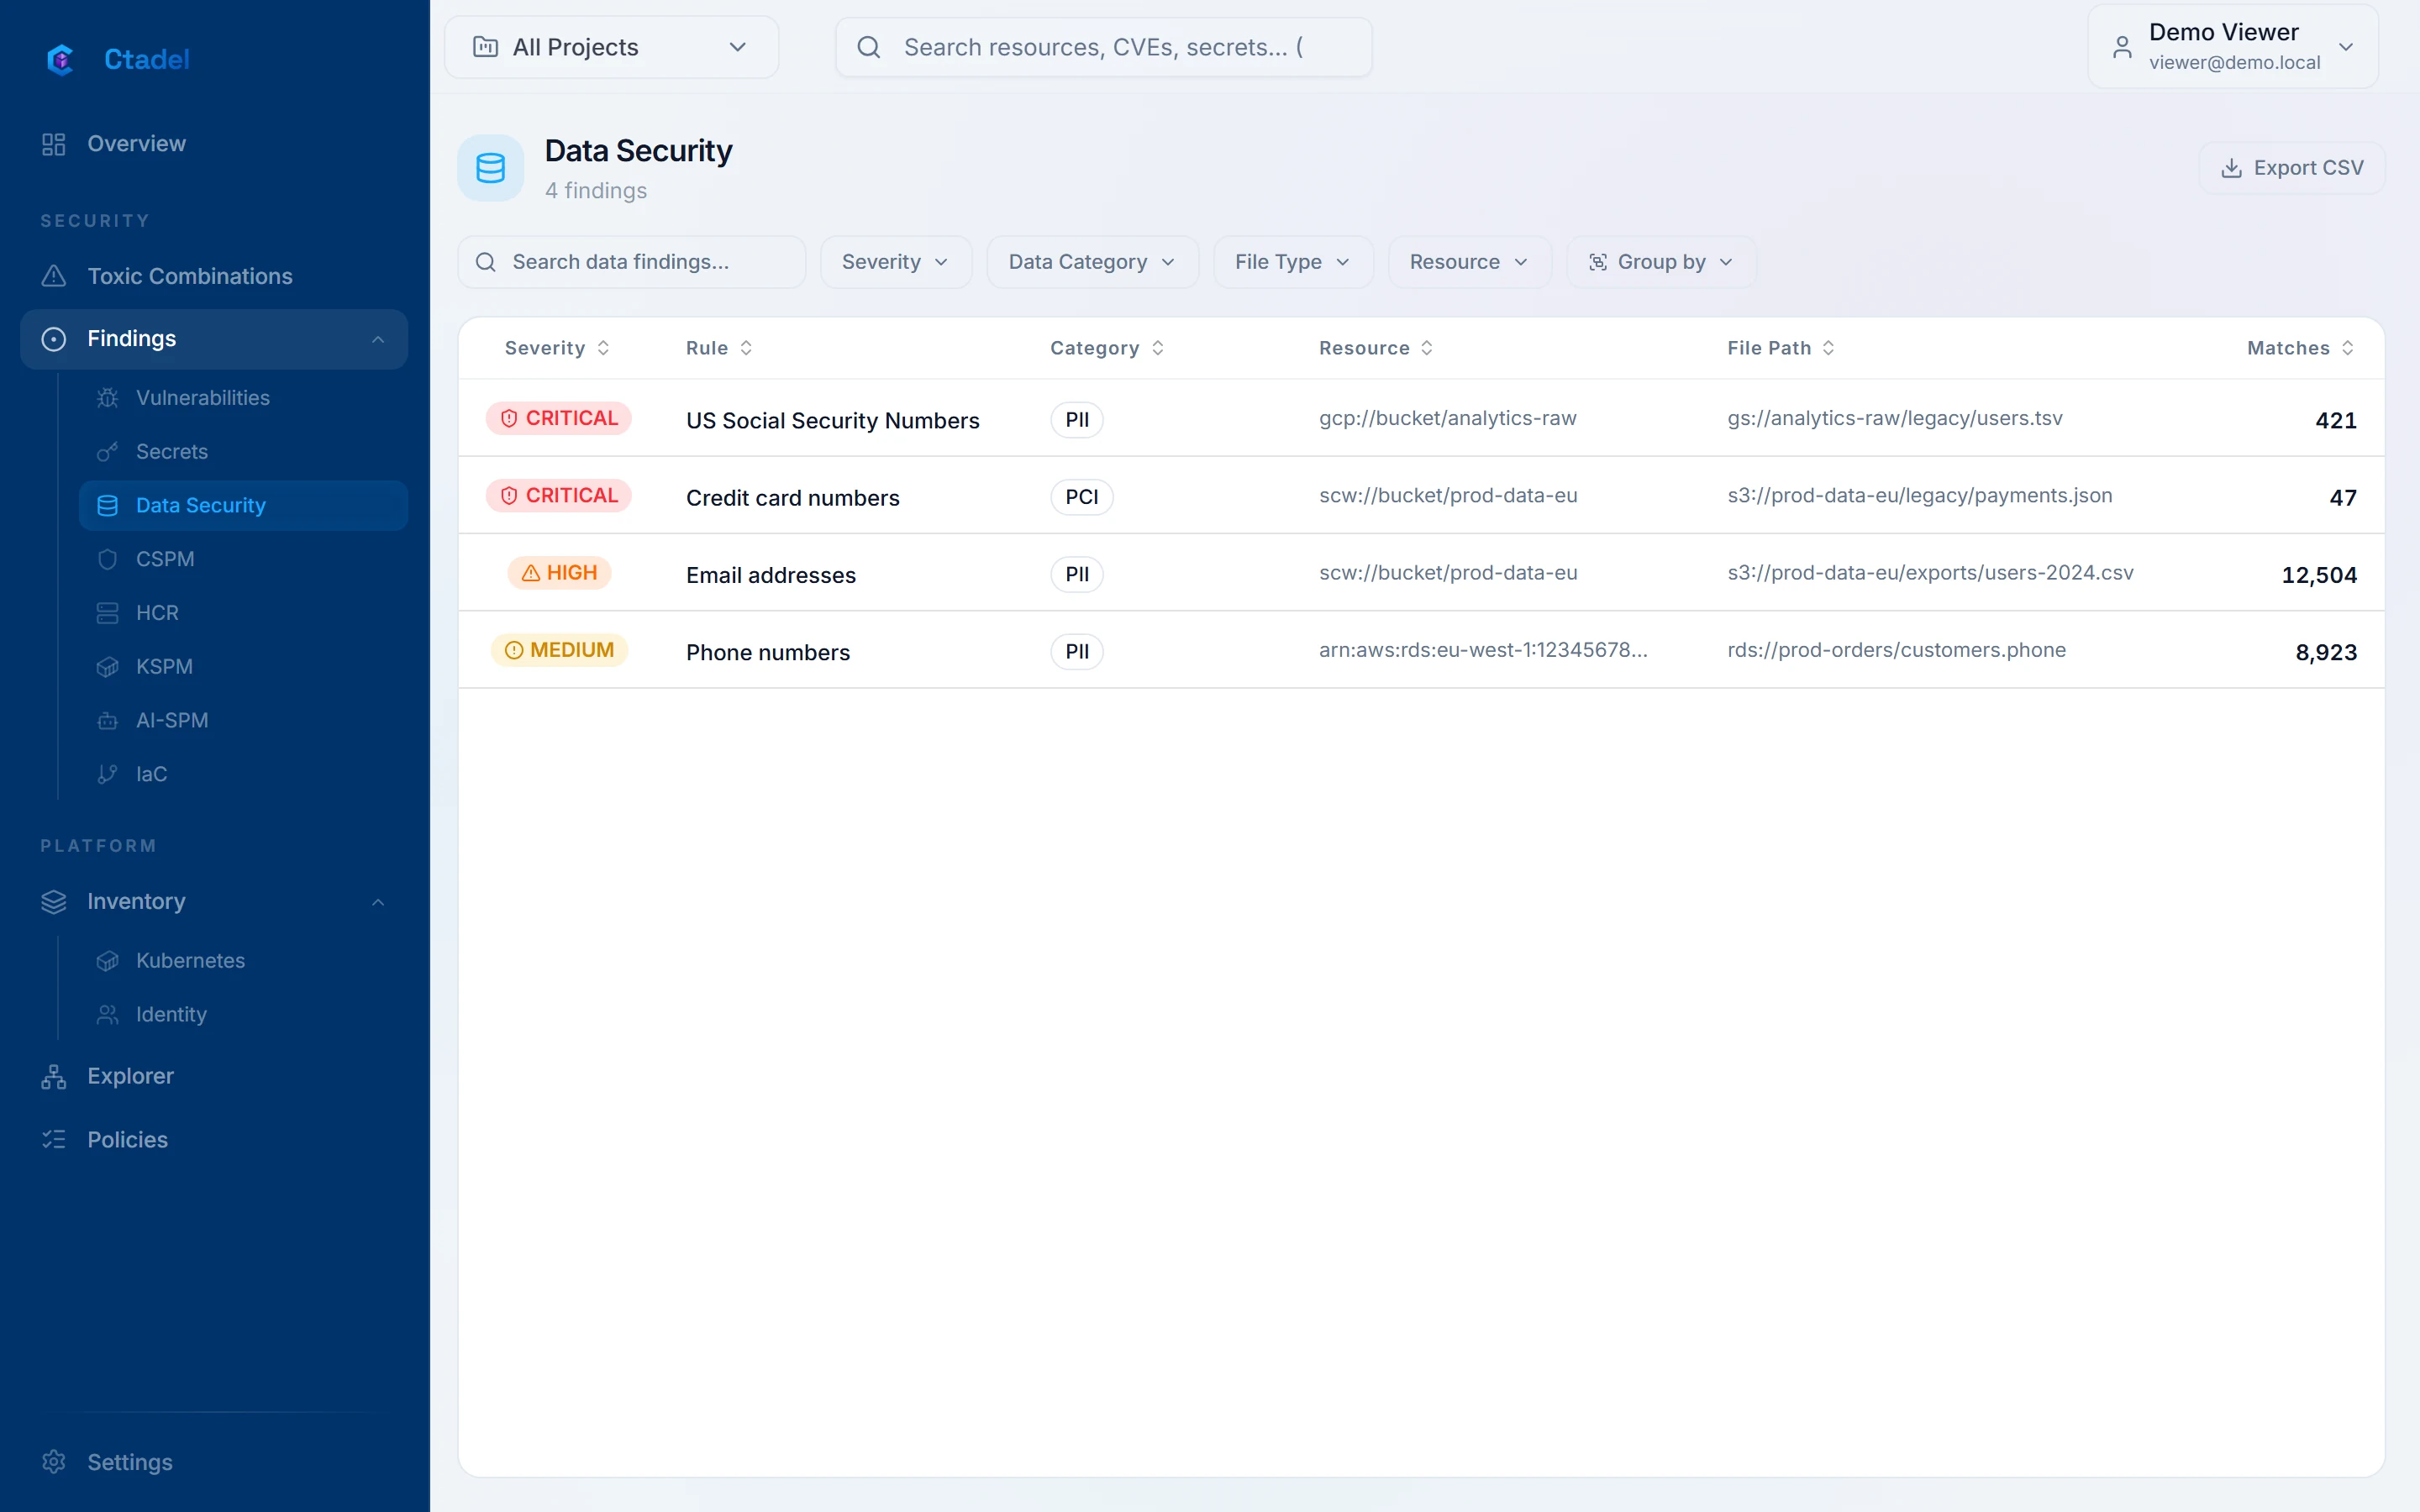
- What is read
- Personal, banking and health data and secrets in objects and tables.
- How
- Objects read by sampling; databases copied temporarily inside your account, read then destroyed. Only masked excerpts are kept.
- In the application
- Data page: matches by category, masked excerpts, estimated volume per resource.
What it cannot see. The formats read are text, archives and common office documents. An encrypted file or a proprietary format is not analysed.
Example detections
- IBAN in a public bucket
- Personal-data database without encryption
- Snapshot containing personal data shared with another account
The other modules
Ready to see this module on your accounts?
The public demonstration runs on fictitious data. For an instance on your own accounts, request a demonstration.