
SCA
Vulnerable packages, with what you need to prioritise
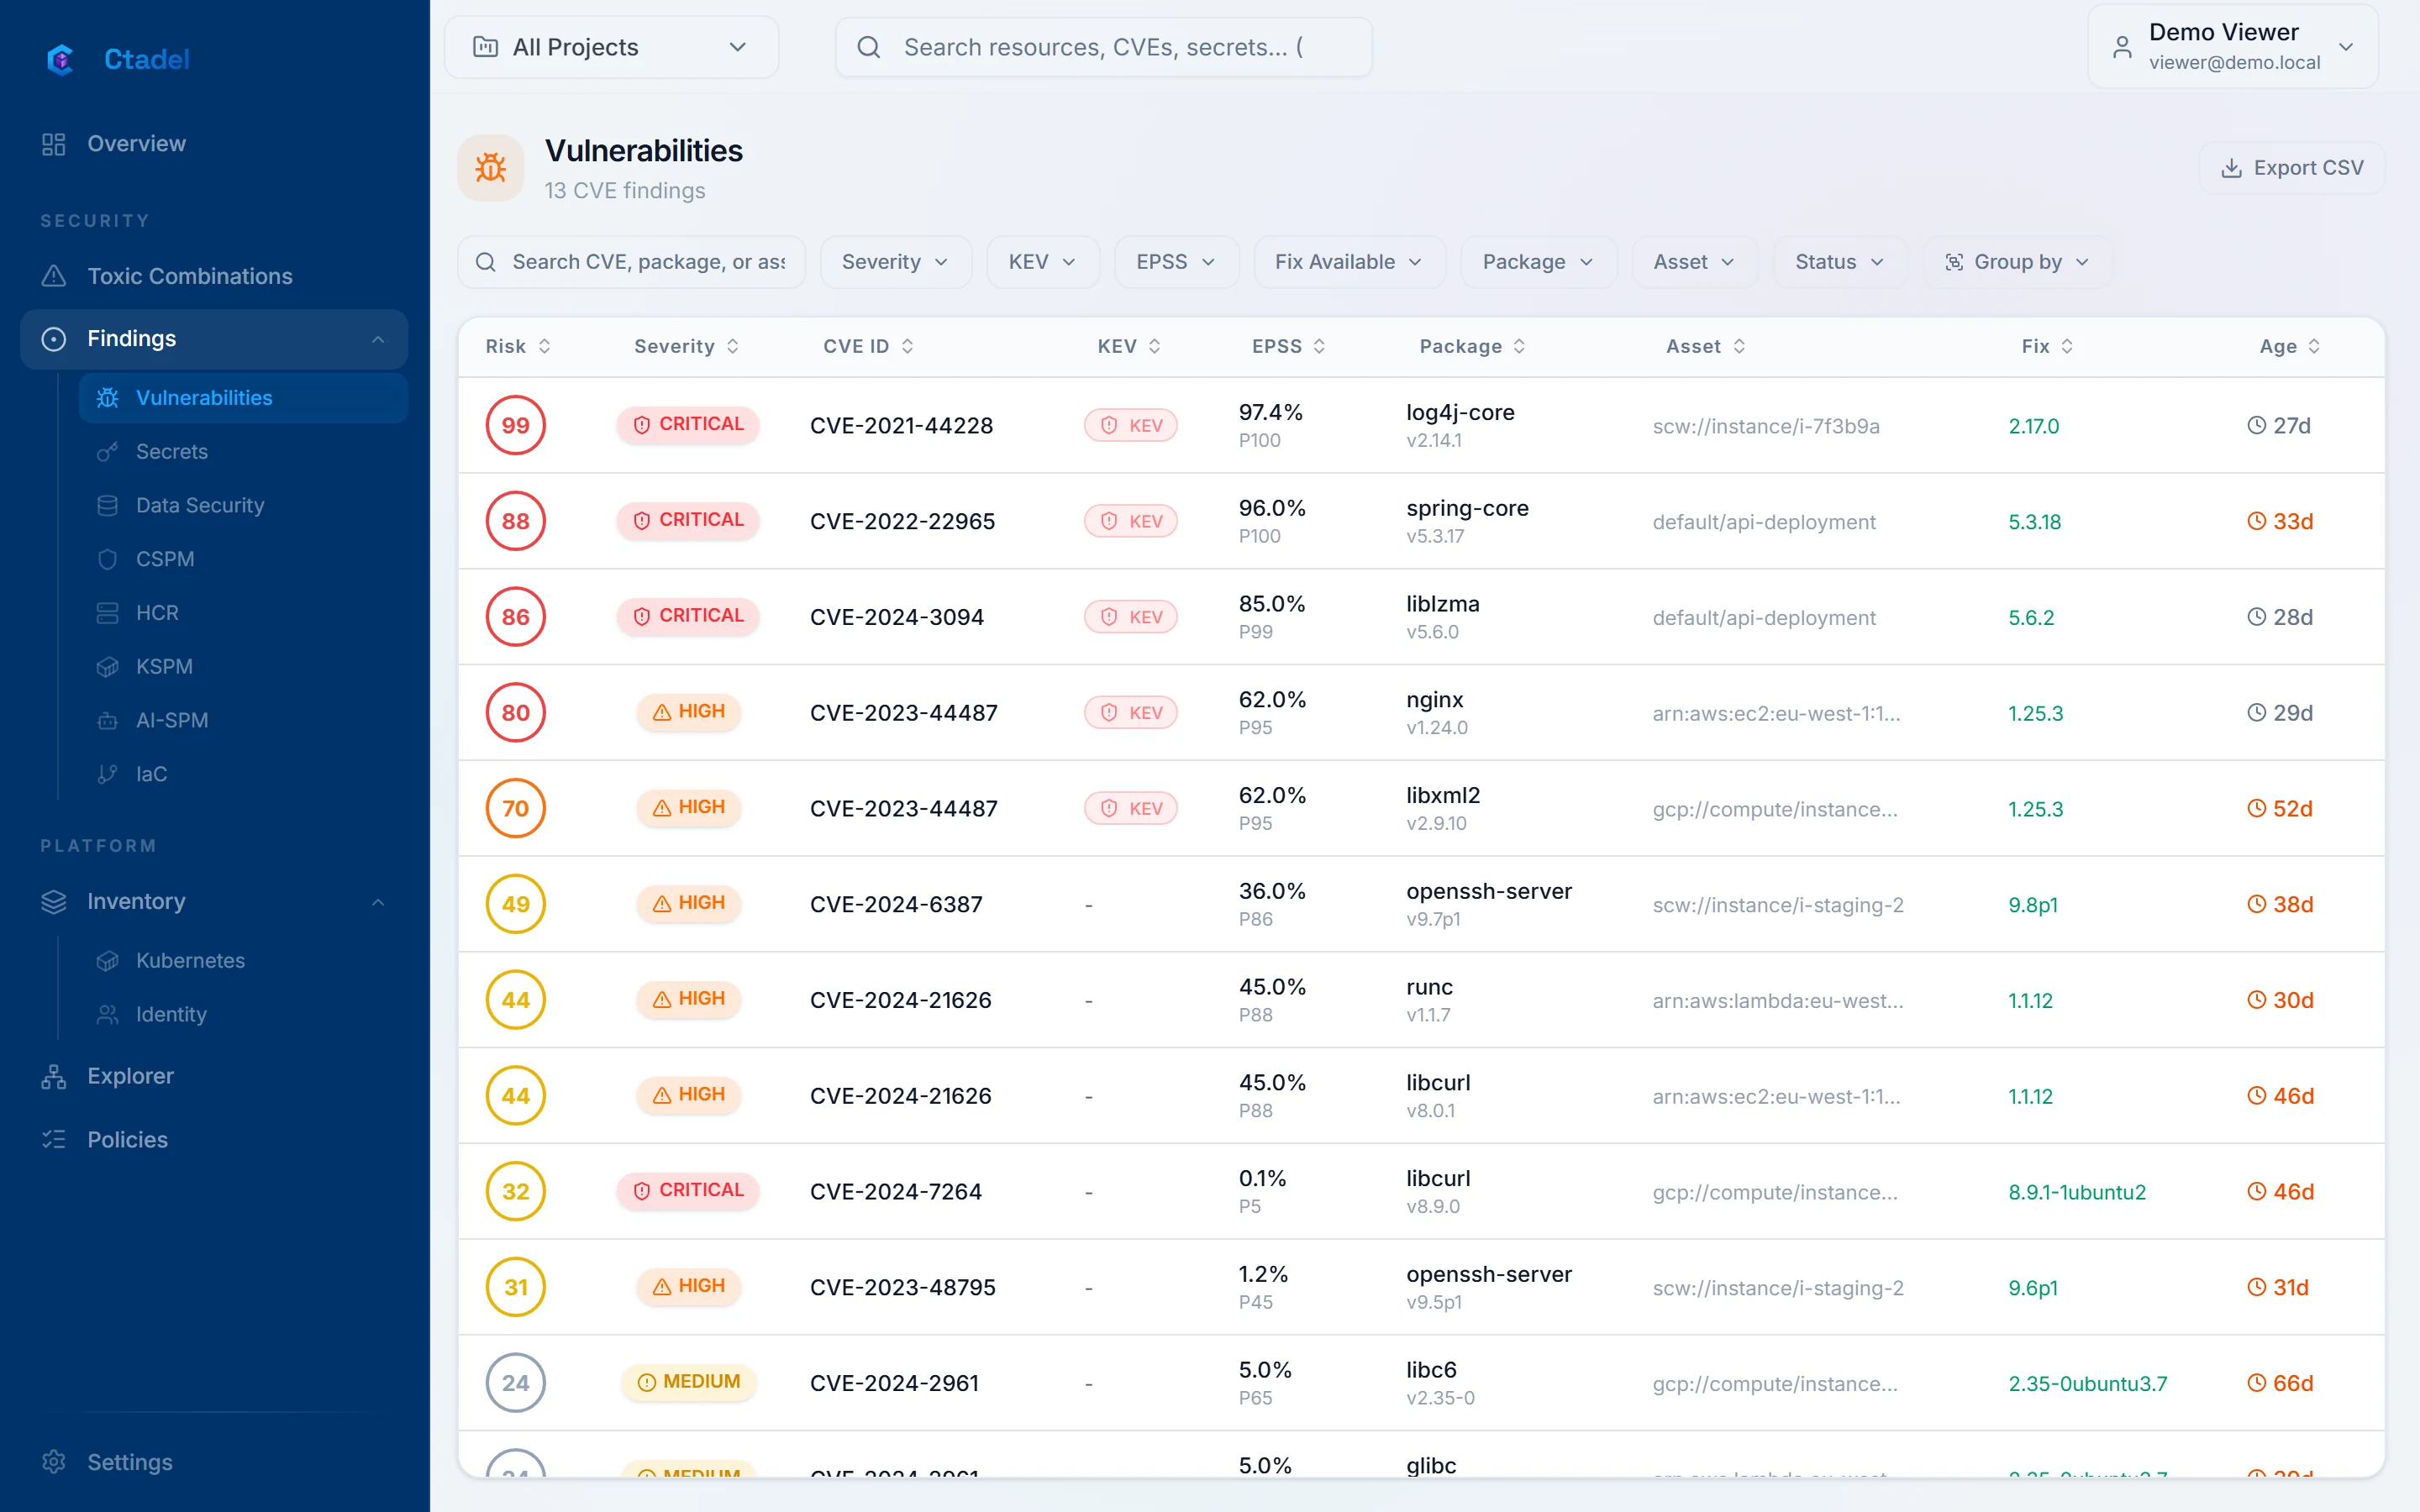
A critical CVE on a private machine and the same one on a public machine are not handled in the same order. Ctadel matches the NVD, the KEV catalogue and the EPSS score with the exposure of the resource in the graph.
- What is read
- Packages on disks, container images, repository dependencies.
- How
- Matched against the NVD, the KEV catalogue and the EPSS score; the exposure of the resource is taken into account.
- In the application
- Vulnerabilities page: by CVE and by package, filtered by cloud or by repository, with the exposure of the resource.
What it cannot see. A vulnerability without a known affected version is listed without a verdict.
Example detections
- Log4Shell (CVE-2021-44228) on an exposed instance
- Compromised xz library in an image
- Vulnerable libcurl version on a public machine
The other modules
Ready to see this module on your accounts?
The public demonstration runs on fictitious data. For an instance on your own accounts, request a demonstration.