
KSPM
Your managed clusters, read through their API
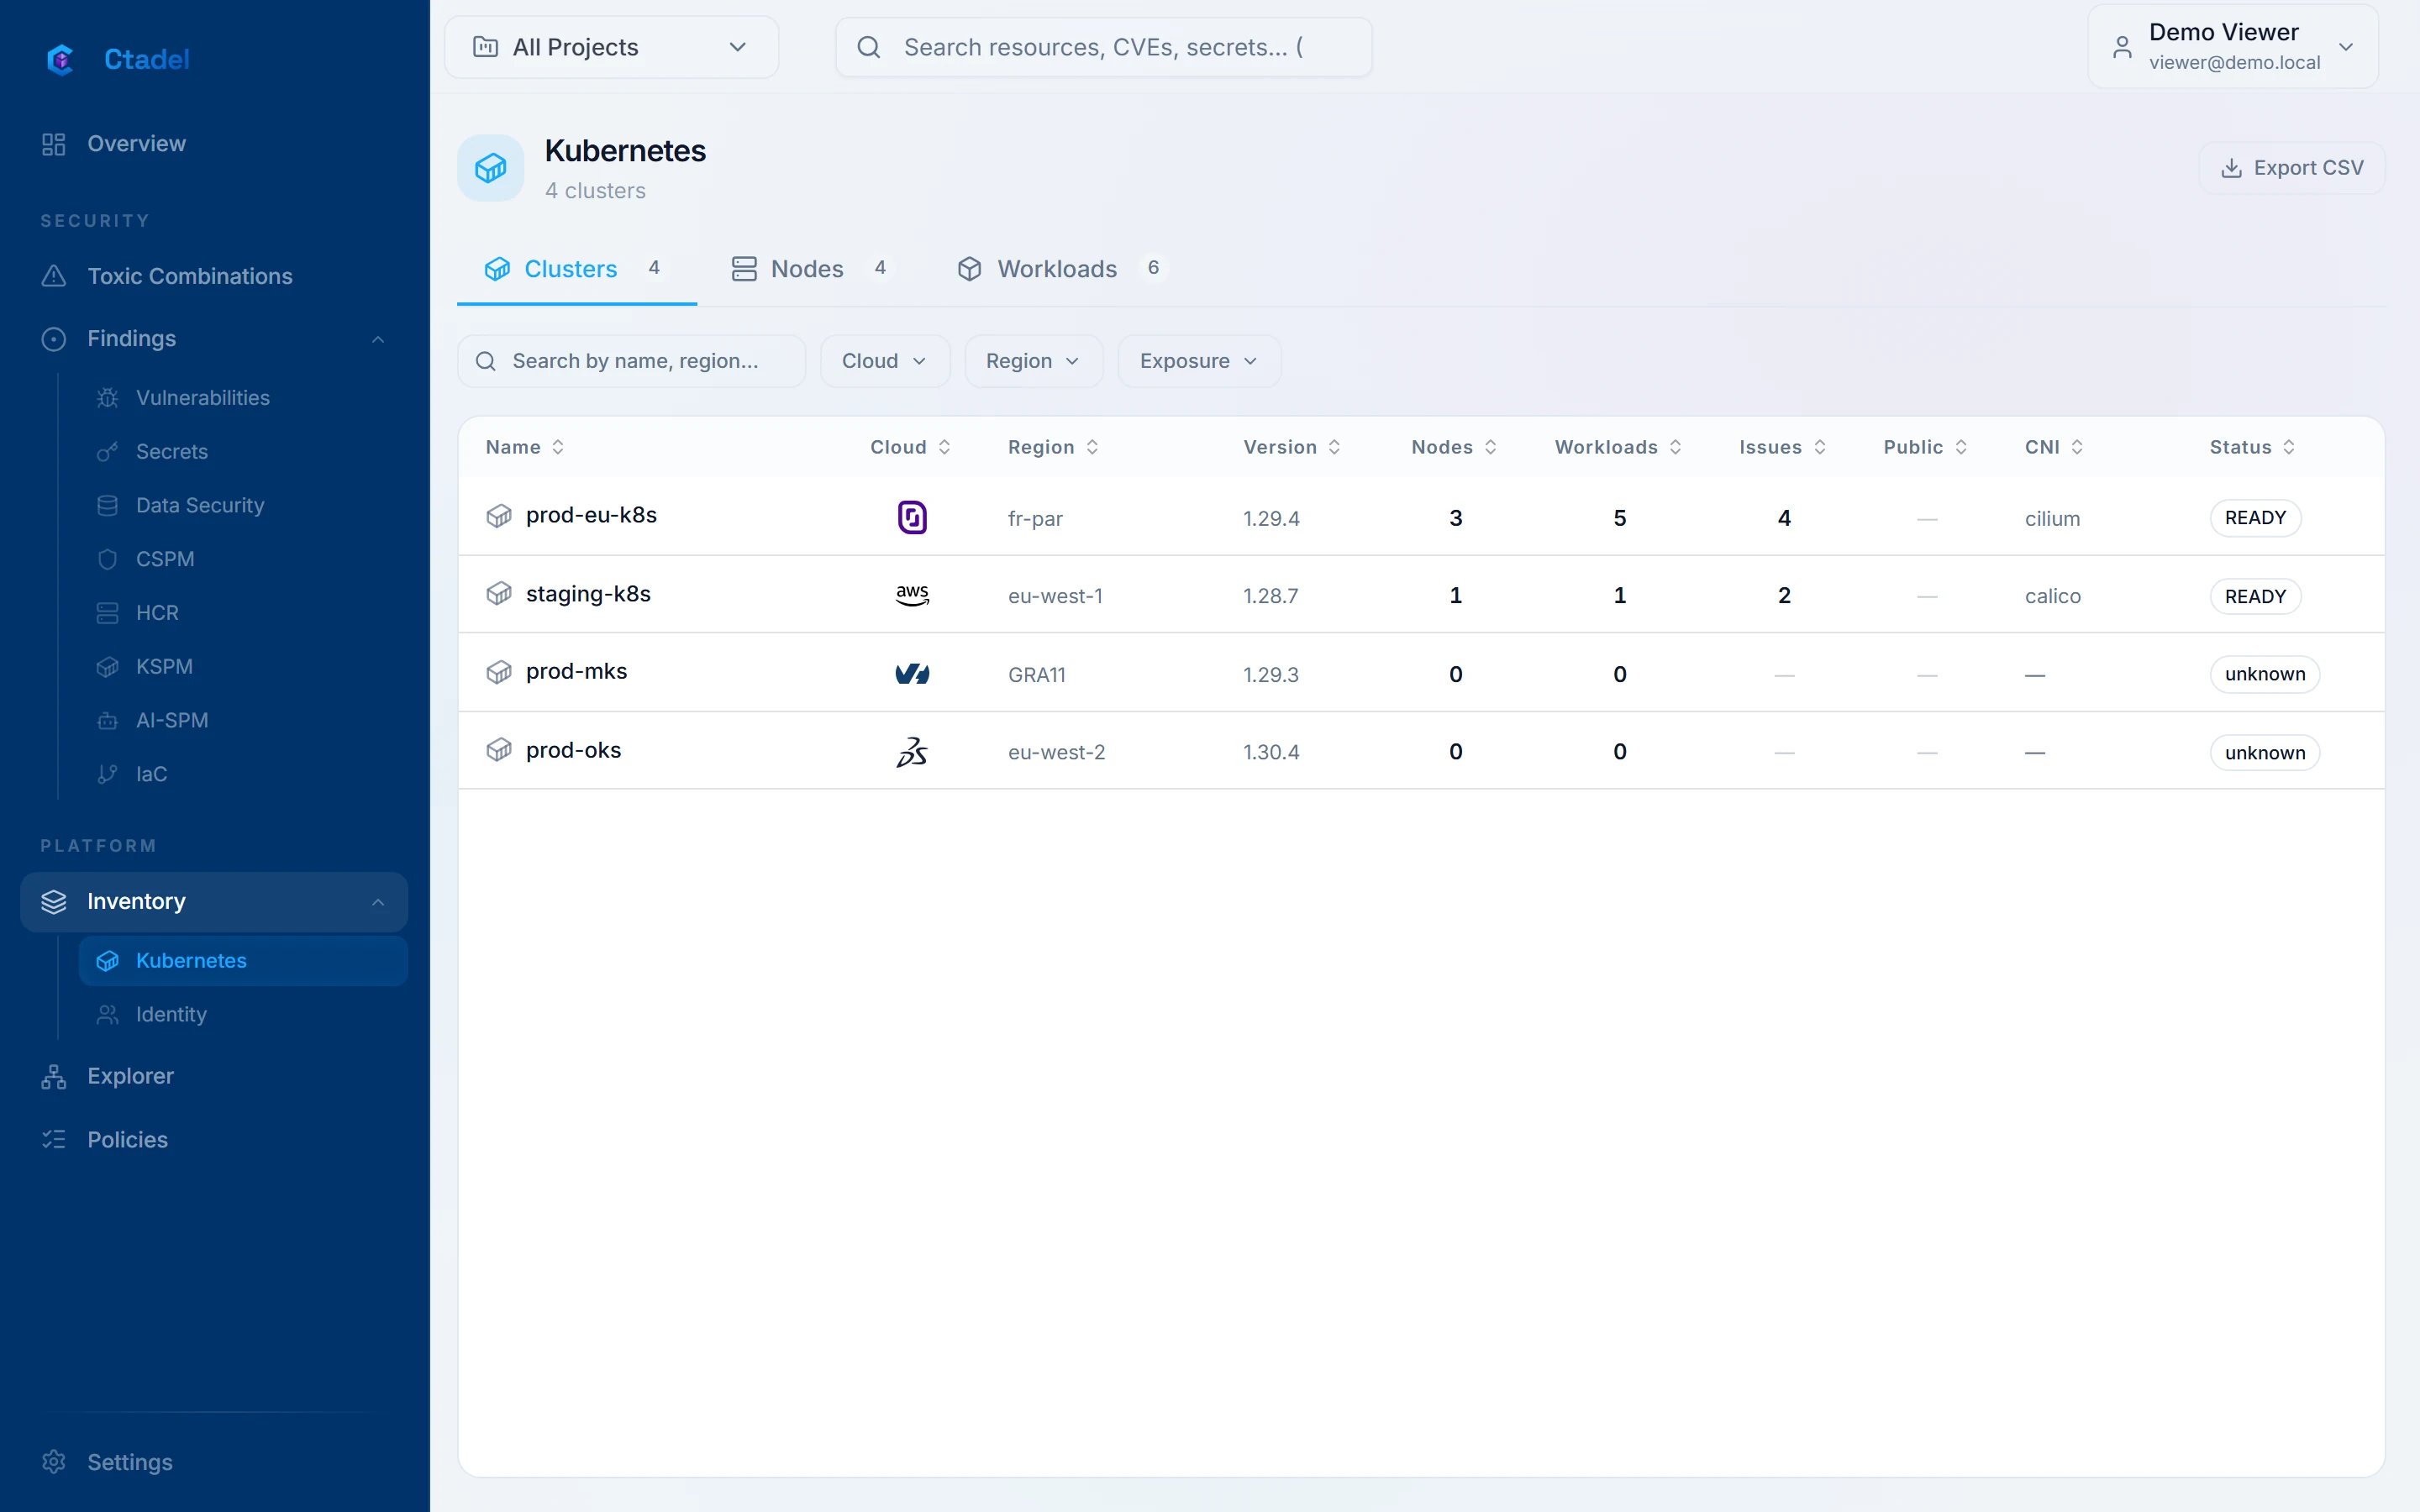
EKS, AKS, GKE, Kapsule, MKS and OKS with a dedicated read-only group, never admin. Workloads, service accounts, RBAC, network policies, images and their vulnerabilities, in the same graph as the cloud that hosts them.
- What is read
- Workloads, service accounts, RBAC, network rules, images, nodes.
- How
- Cluster API through a dedicated read-only group; images scanned for vulnerabilities.
- In the application
- Kubernetes and KSPM pages: clusters, nodes, workloads, findings per cluster and per namespace.
What it cannot see. Rules that require access to the node itself, outside the API, are disabled.
Example detections
- Privileged container
- Kubernetes dashboard exposed
- API server without address restriction
The other modules
Ready to see this module on your accounts?
The public demonstration runs on fictitious data. For an instance on your own accounts, request a demonstration.