Public Cloud, dedicated servers, Managed Kubernetes, buckets: Ctadel reads your OVHcloud accounts through the API with a read-limited consumer key, and applies the same scanners as everywhere else.
An optional S3 key pair lets the Data and Secrets scanners read bucket contents.
What you get
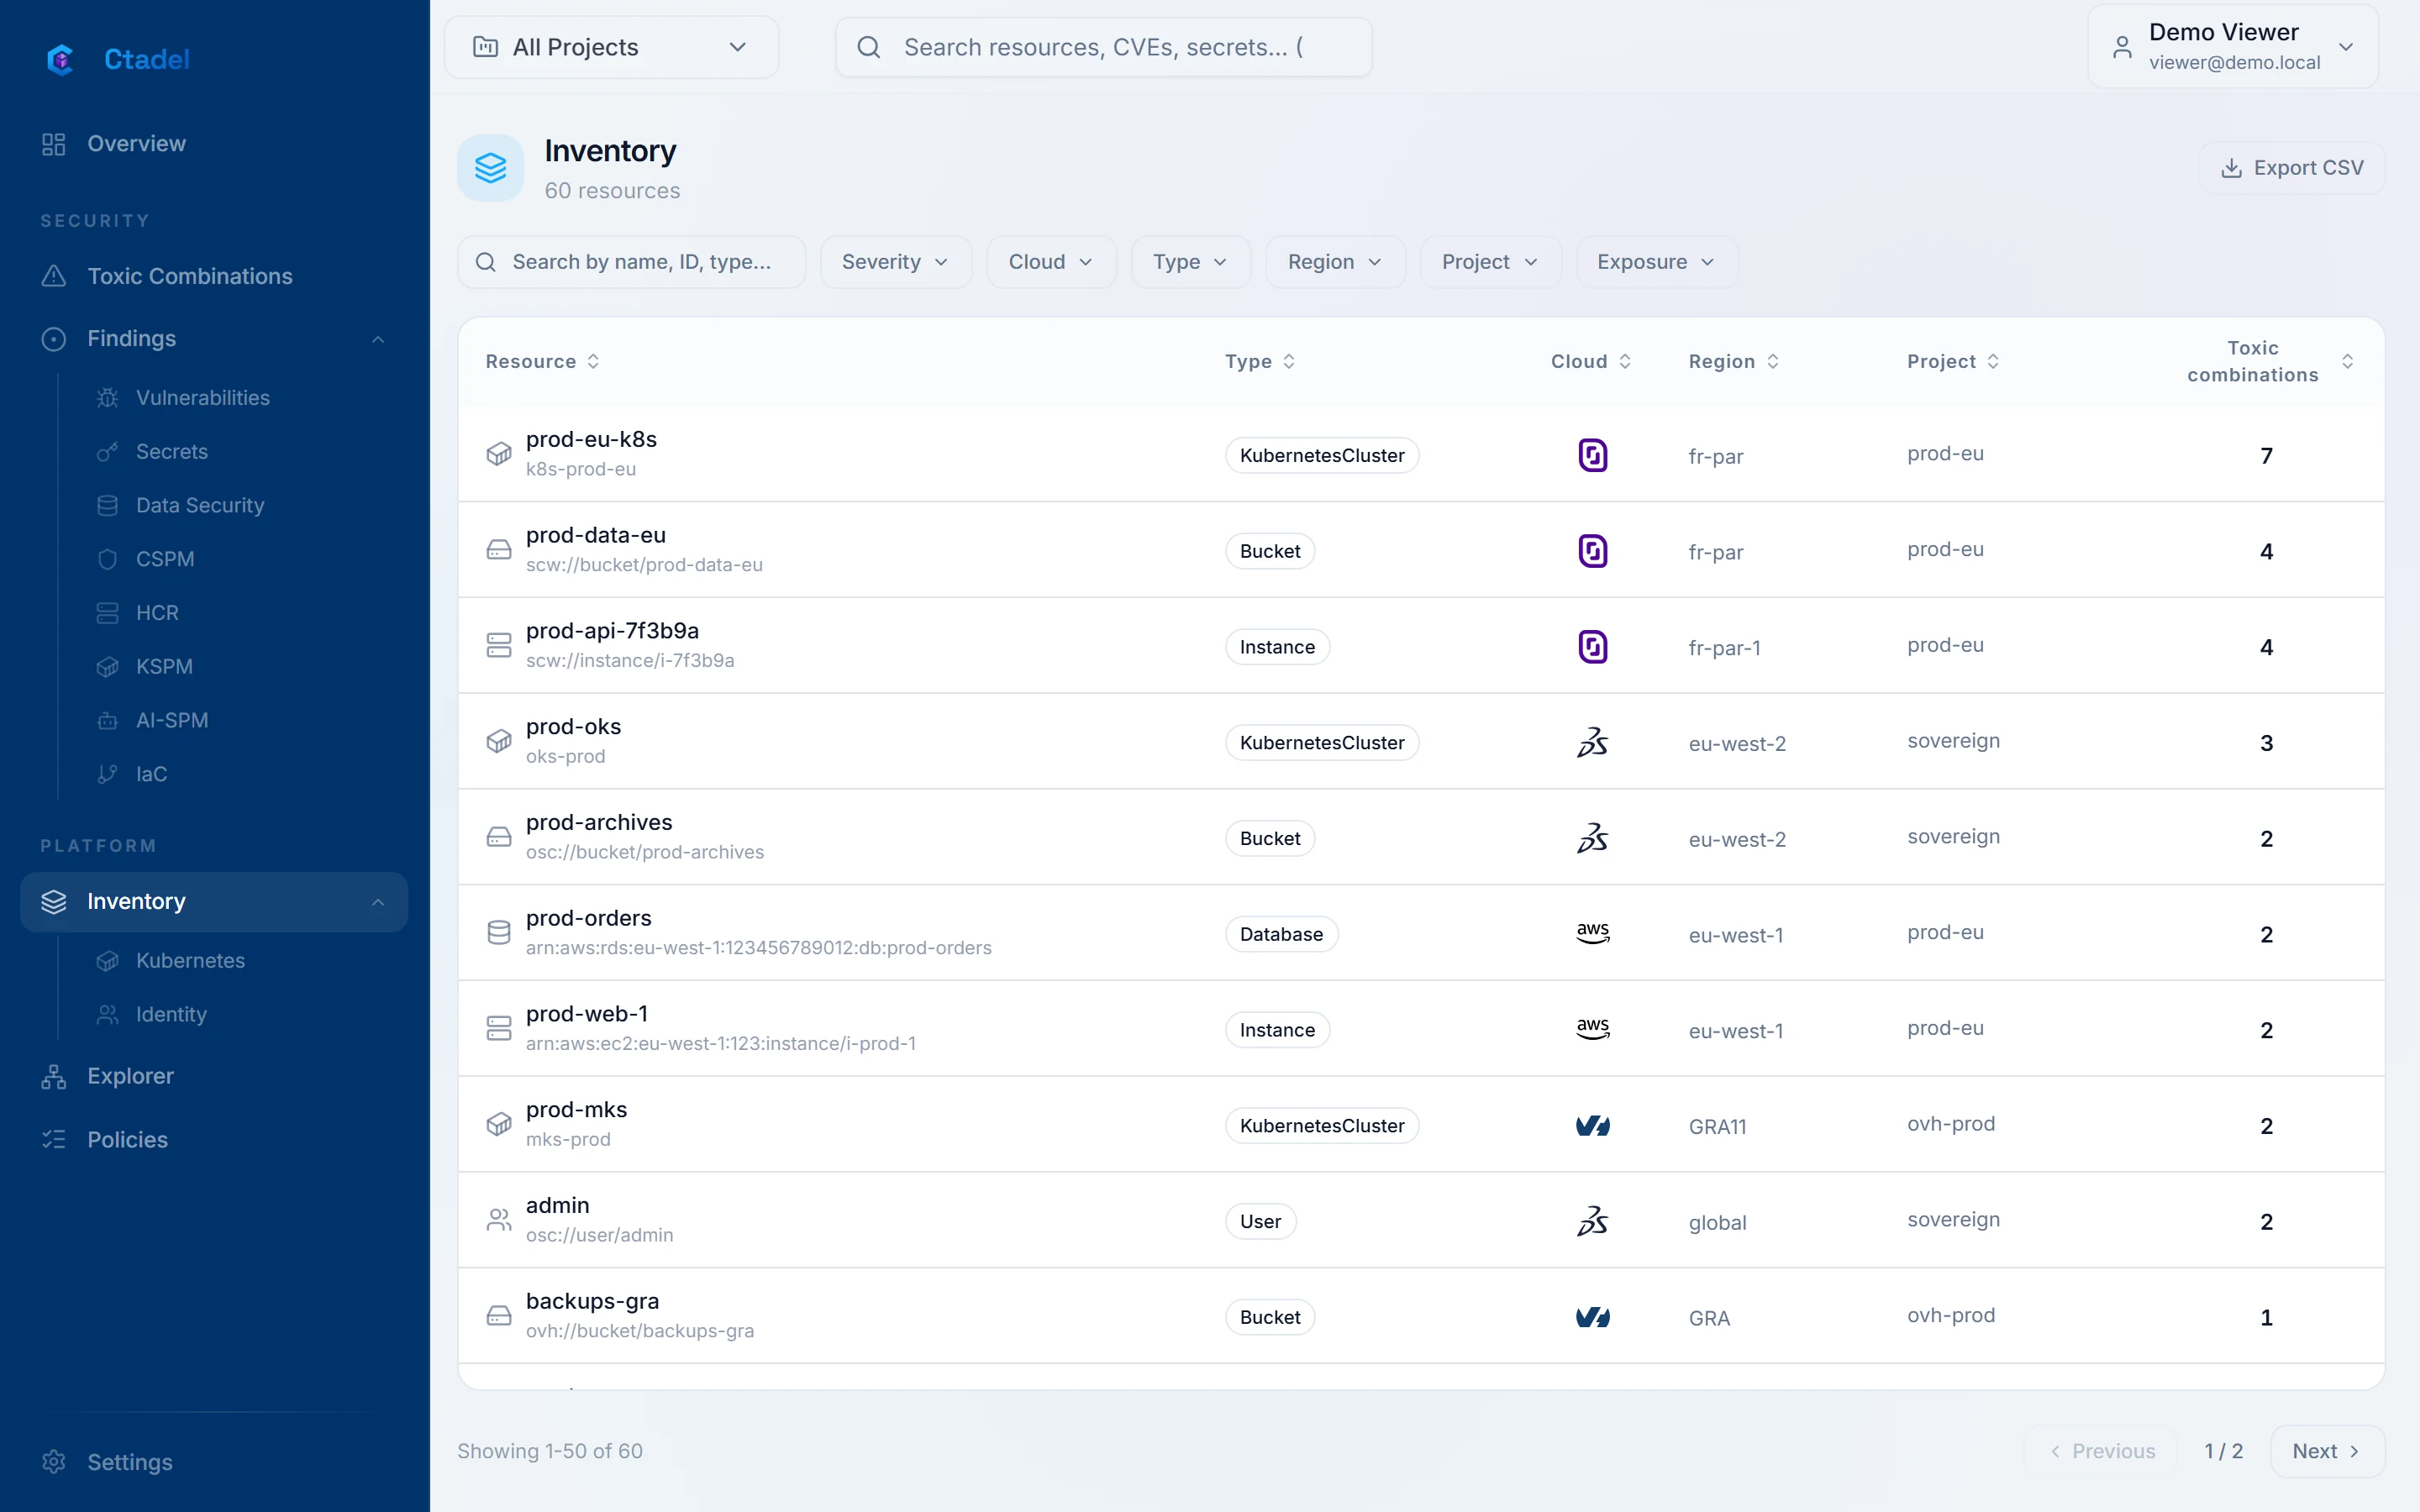
Configuration, identities, sensitive data, secrets, vulnerabilities of instances and dedicated servers, managed Kubernetes and toxic combinations, in the same findings list and graph as your other clouds.
Dedicated servers inventoried alongside Public Cloud
MKS read through the cluster API
OVH provider Terraform analysed on every pull request
The access requested
An API application with a consumer key limited to GET calls on /me, /cloud/project, /dedicated/server, /domain, /ip and /iam. Disk and database analysis requires additional copy permissions in the project.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.