A service principal with read access to the subscription is enough to inventory Azure; Entra ID identities are matched with those of your other clouds.
Virtual machines, disks and snapshots, storage accounts, Key Vault and Managed HSM, AKS, SQL, flexible PostgreSQL, Cosmos DB, Entra ID (users, service principals, role assignments), Defender, activity log, Monitor, networks and NSGs, Azure Firewall, Application Gateway, Front Door, API Management, Functions, App Service, Azure OpenAI and cognitive services, Synapse, Data Factory, HDInsight, Recovery Services.
What you get
The posture of each subscription, effective permissions of role assignments, sensitive data in storage accounts and databases, secrets, virtual machine vulnerabilities, Azure OpenAI and AI Search services, and toxic combinations.
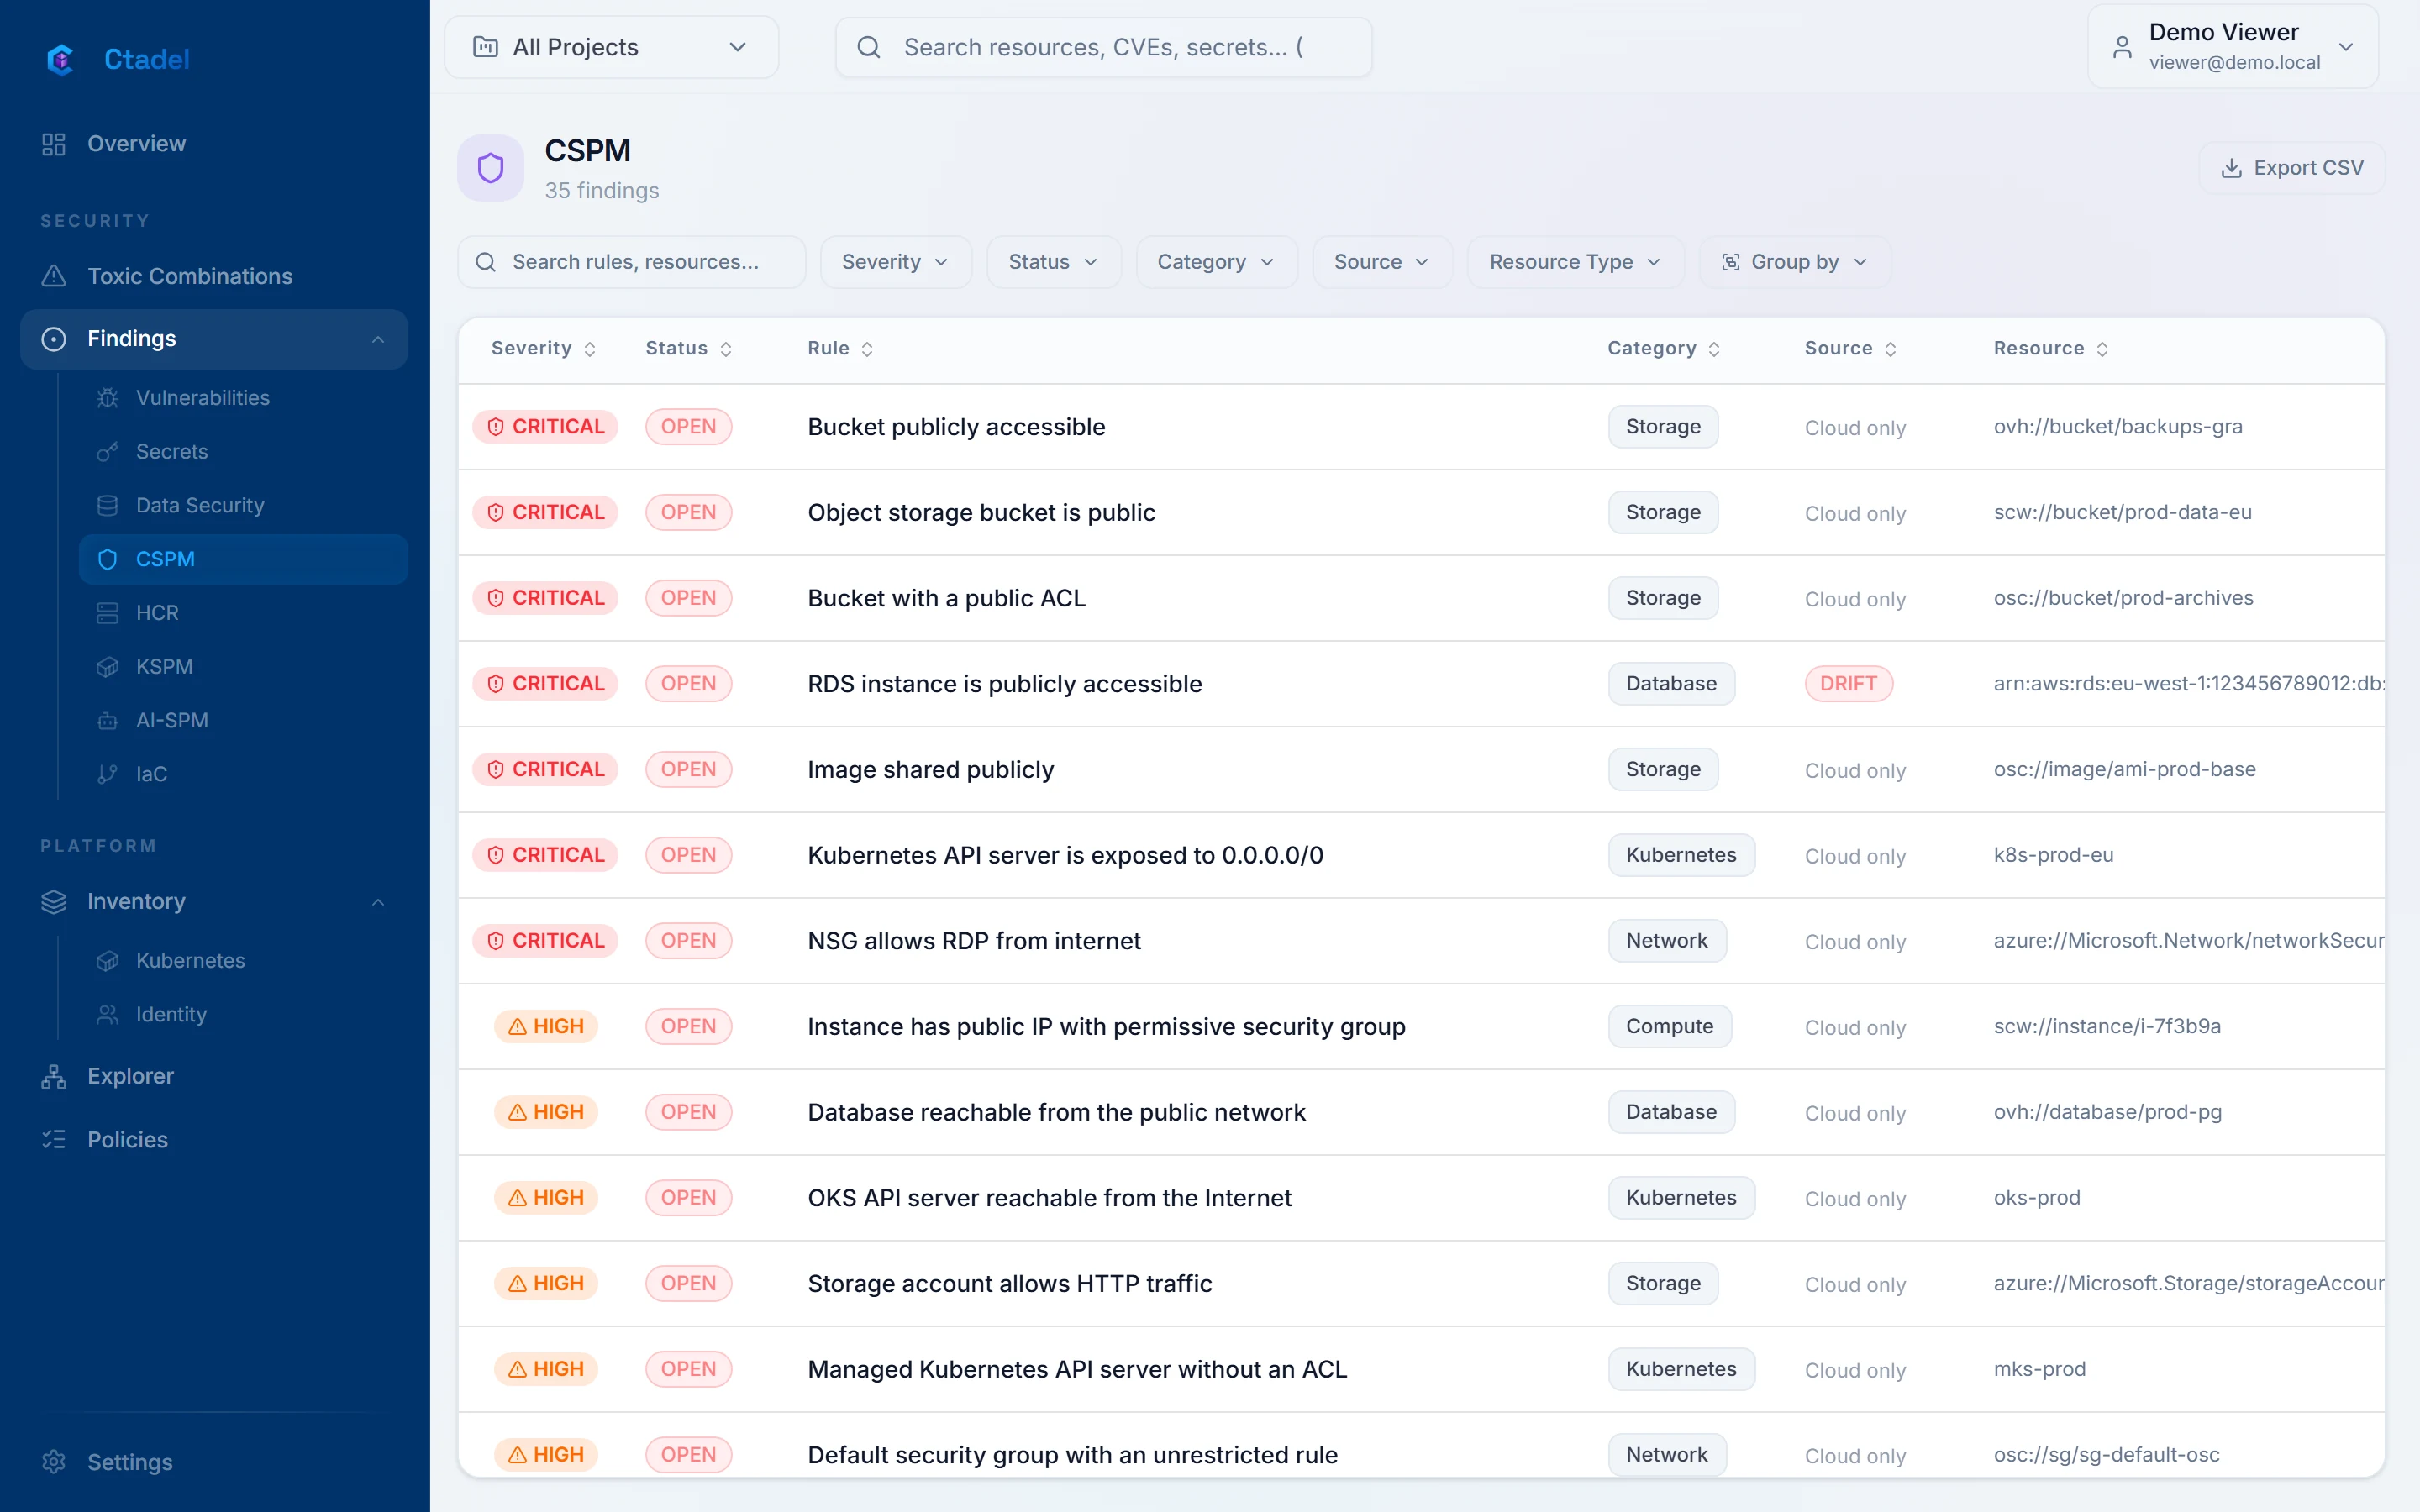
Open NSGs, public storage accounts, Key Vault without purge protection
AKS read through the cluster API
azurerm Terraform analysed on every pull request
The access requested
A service principal (tenant, client, secret) with read access to the subscription. Disk and database analysis requires additional copy permissions; for AKS, the worker obtains the kubeconfig through listClusterAdminCredential, or uses a kubeconfig you provide.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.