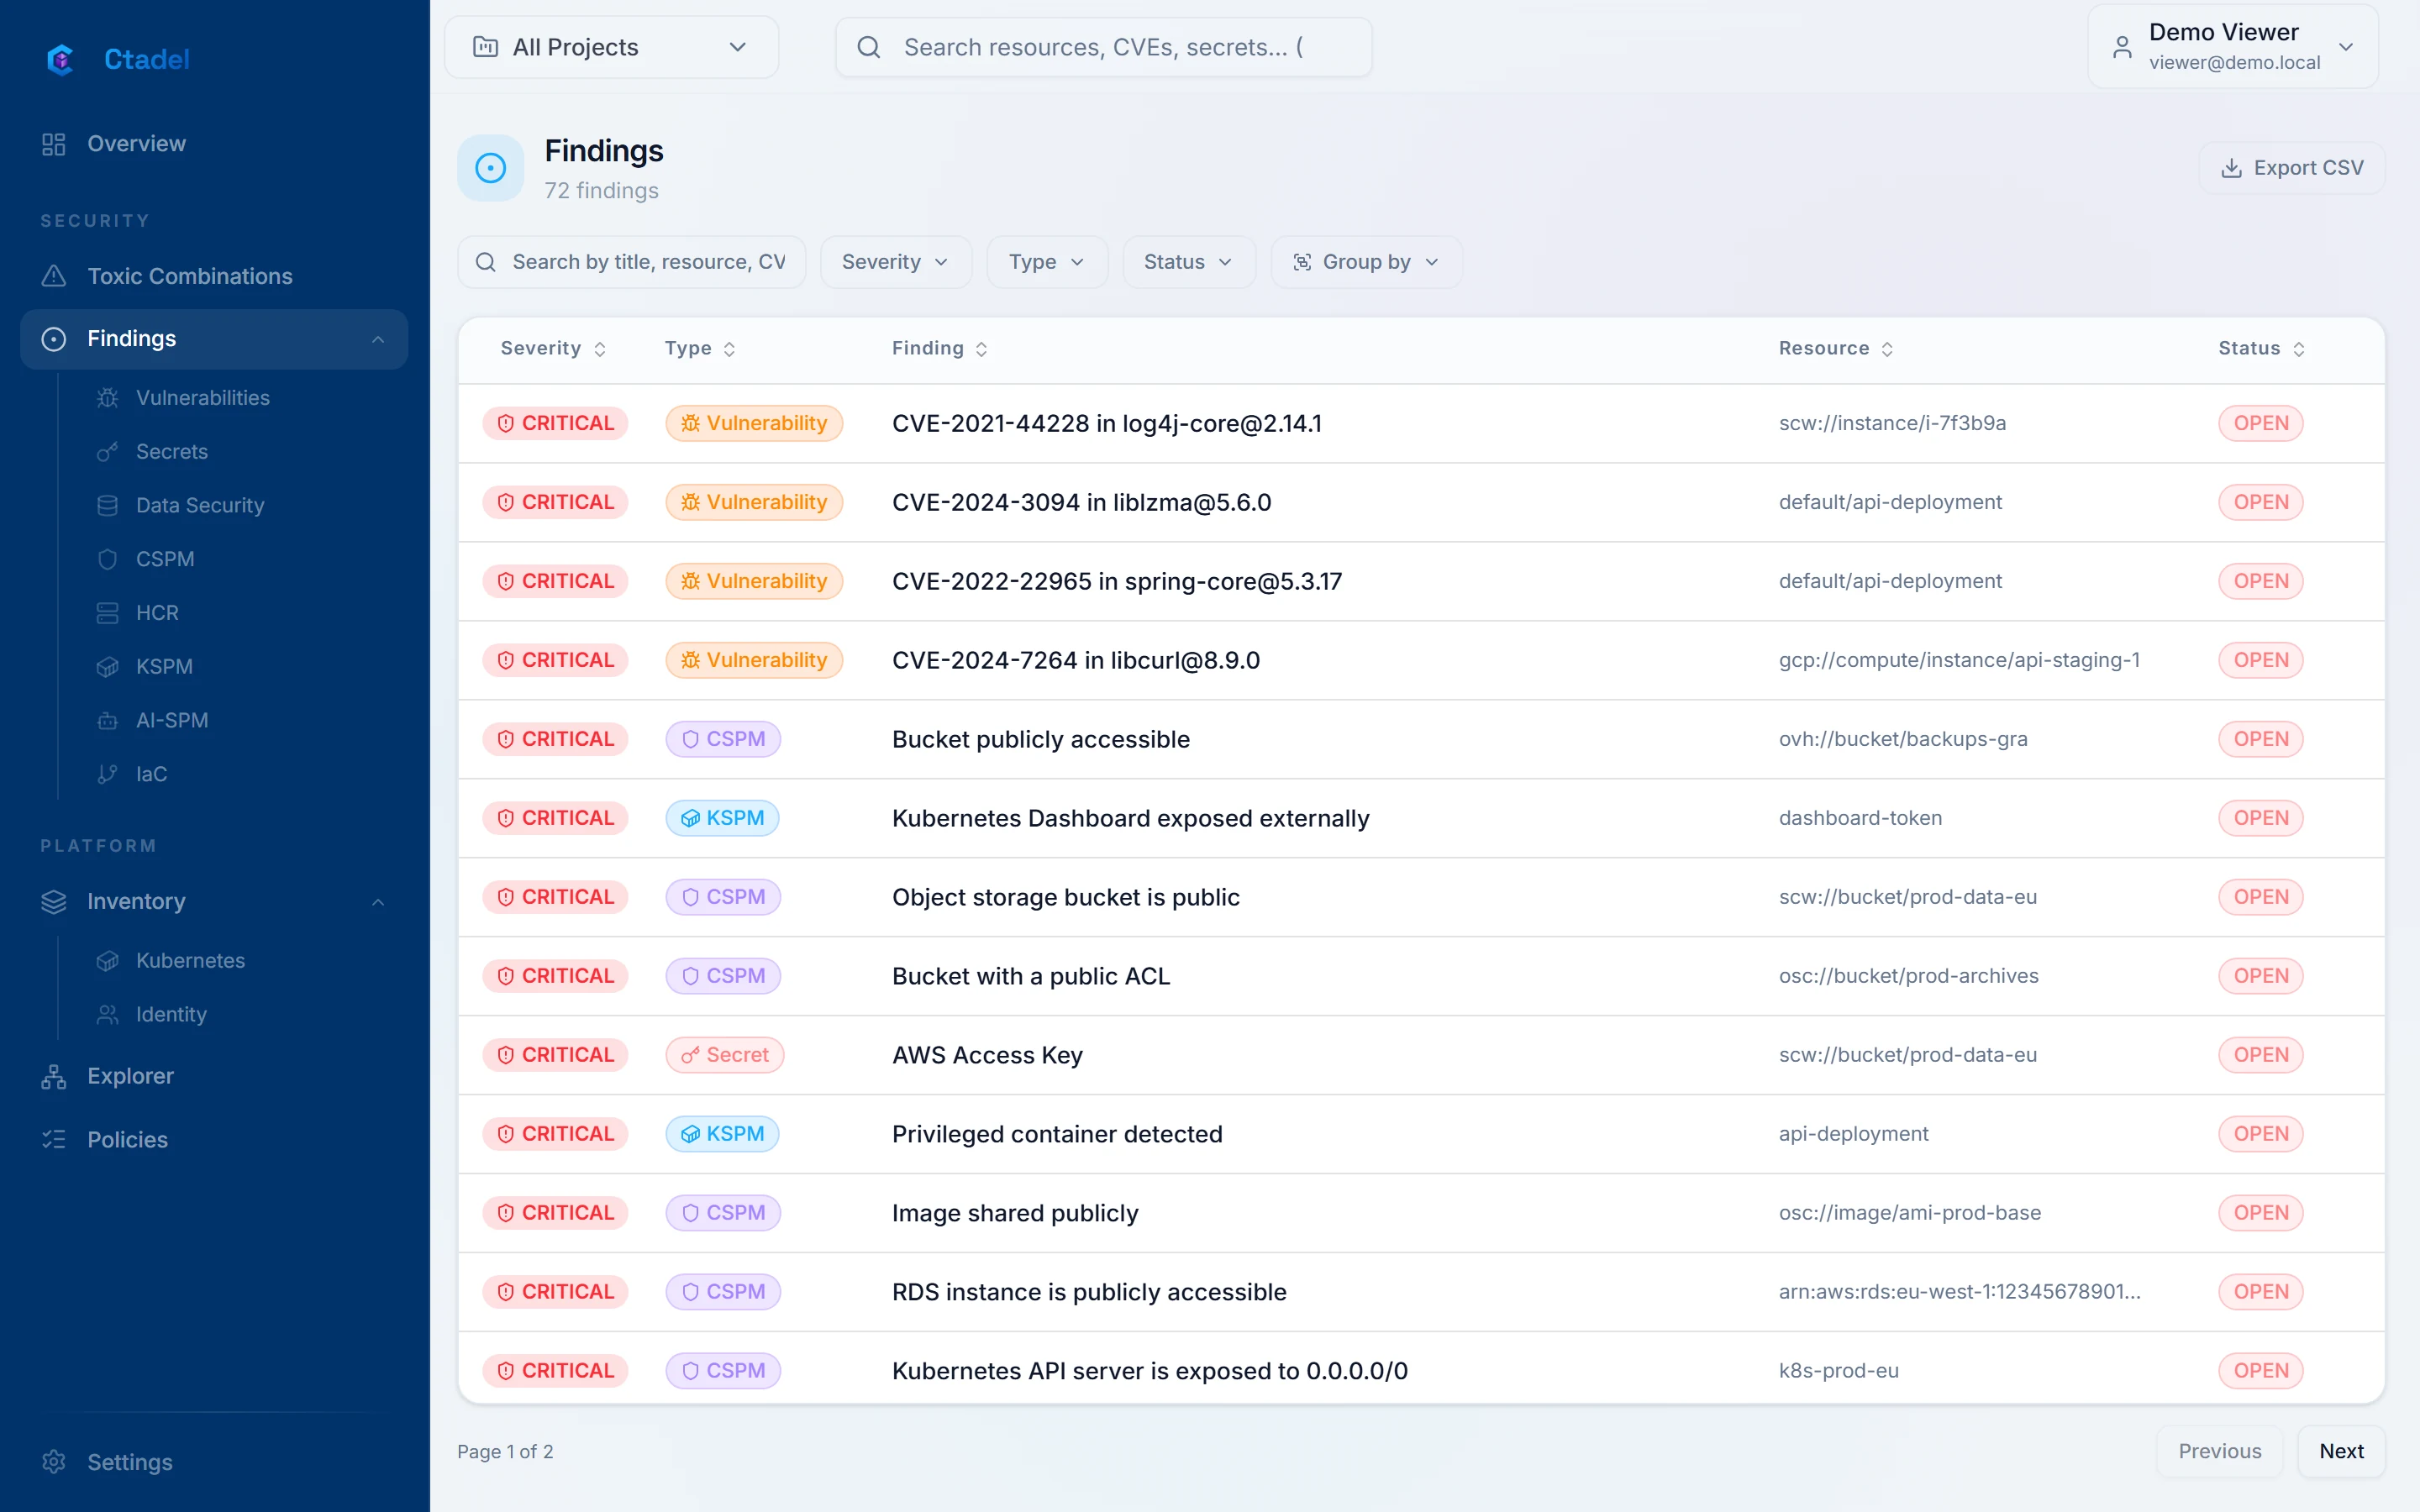
PCI DSS v4.0, checked on the cardholder data environment
PCI DSS requires strict segmentation, encryption, restricted access and documented vulnerability management. Ctadel checks these requirements on your clouds and cites the requirement number on every finding.
Open security groups and firewalls (requirement 1), encryption at rest and in transit (3 and 4), accounts and permissions (7 and 8), logging (10), vulnerabilities with exploitability (6 and 11). The Data scanner spots card numbers and IBANs in buckets and databases to delimit the scope.
Requirement number cited on every finding
Card data spotted in storage
Attack paths to the resources that hold it
Evidence for the QSA
CSV export of findings with their references, history, audit log. Attack paths document the real segmentation: what is reachable from the internet, and what it reaches.
What Ctadel does not do
Every rule in the catalogue cites the controls of the frameworks it covers. Those references appear in the detail panel of each finding and export with them. Reports per framework are under internal validation; Ctadel claims no certification for itself.
Ctadel is not an ASV and does not perform the quarterly external scans PCI DSS requires.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.