Skip to content
Compliance

ISO 27001, checked on your clouds at every scan

Annex A of ISO/IEC 27001:2022 requires controls on access, encryption, logging, configuration and vulnerability management. Ctadel checks them on your six clouds and cites the control on every finding.

ISO 27001, checked on your clouds at every scan

What Ctadel checks

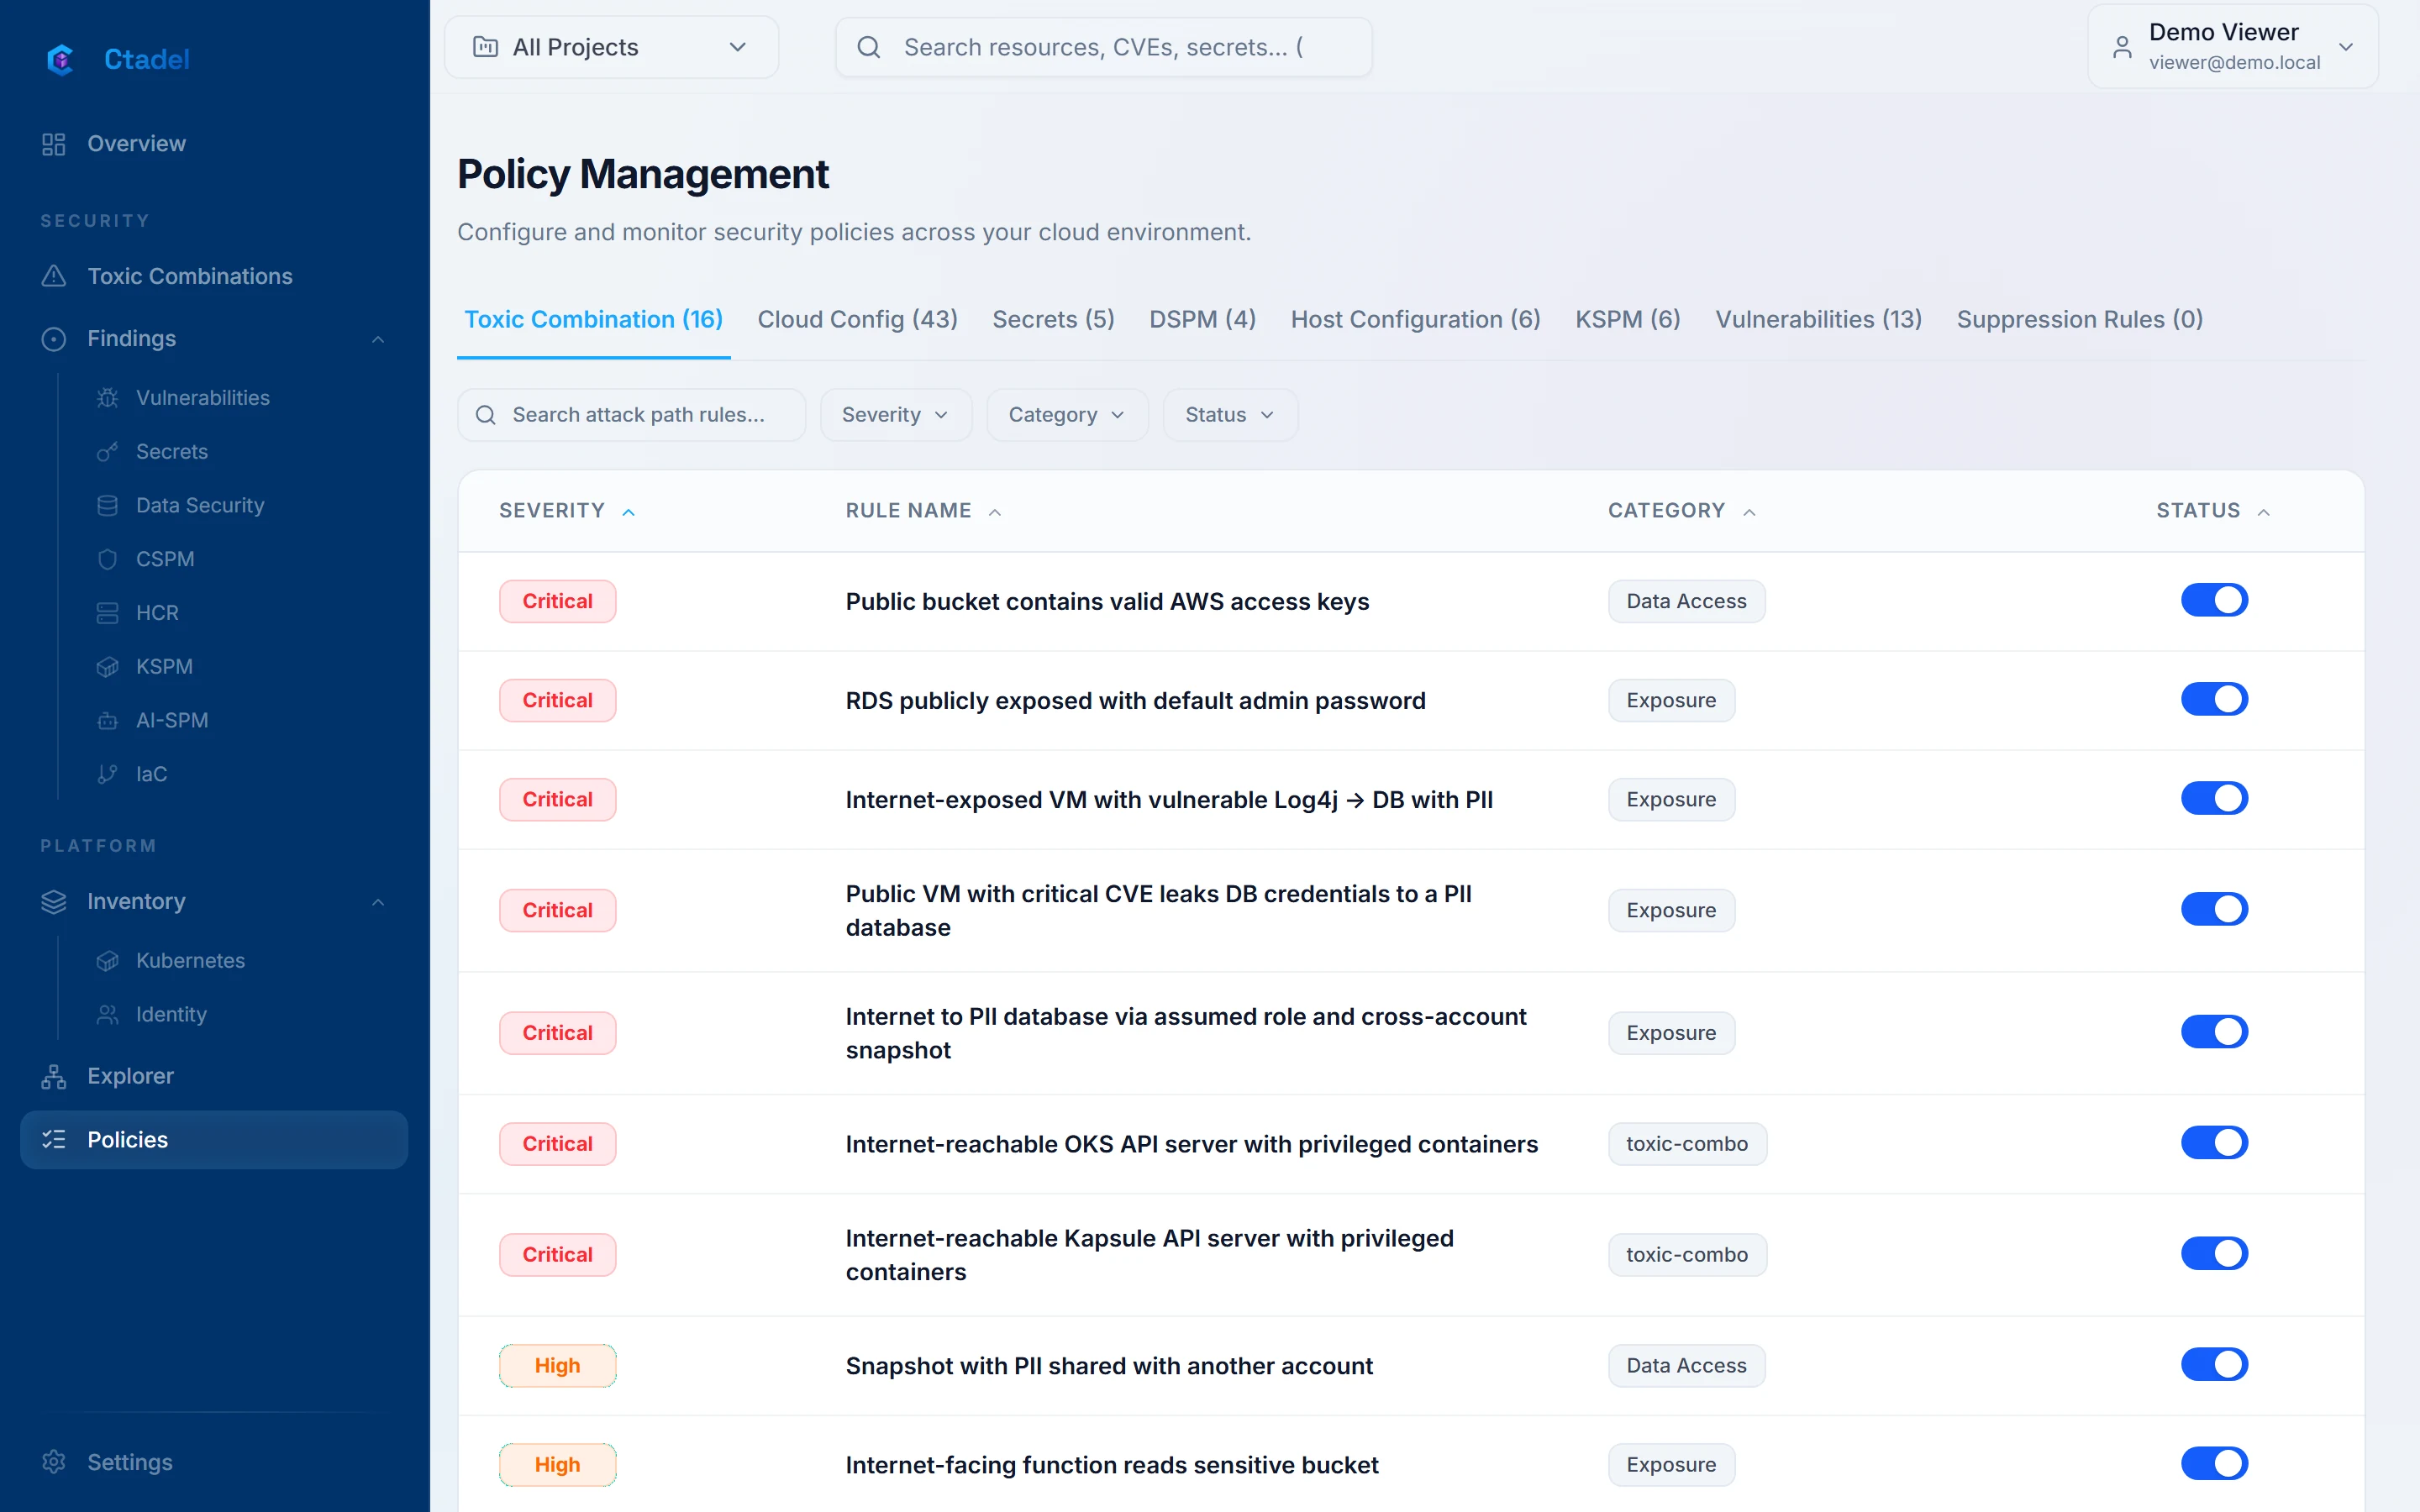
Configuration, Kubernetes, host and data rules carry the reference of the ISO 27001 control they cover: access control (A.5, A.8), cryptography, logging and monitoring, management of technical vulnerabilities, network security. An open finding is a potential non-conformity, with the resource, the rule and the fix.

  • Control reference on every finding
  • Effective permissions of identities for access control
  • Vulnerabilities with exploitability for technical vulnerability management

Evidence for the auditor

Findings export to CSV with their references. The application audit log keeps every user action for one year. The dashboard history shows the day-by-day evolution. The trust centre answers questions about the hosting and data of Ctadel itself.

What Ctadel does not do

Every rule in the catalogue cites the controls of the frameworks it covers. Those references appear in the detail panel of each finding and export with them. Reports per framework are under internal validation; Ctadel claims no certification for itself.

Ctadel covers only the technical side of the controls: policy, organisation and processes remain yours to document.

See it on your accounts

The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.