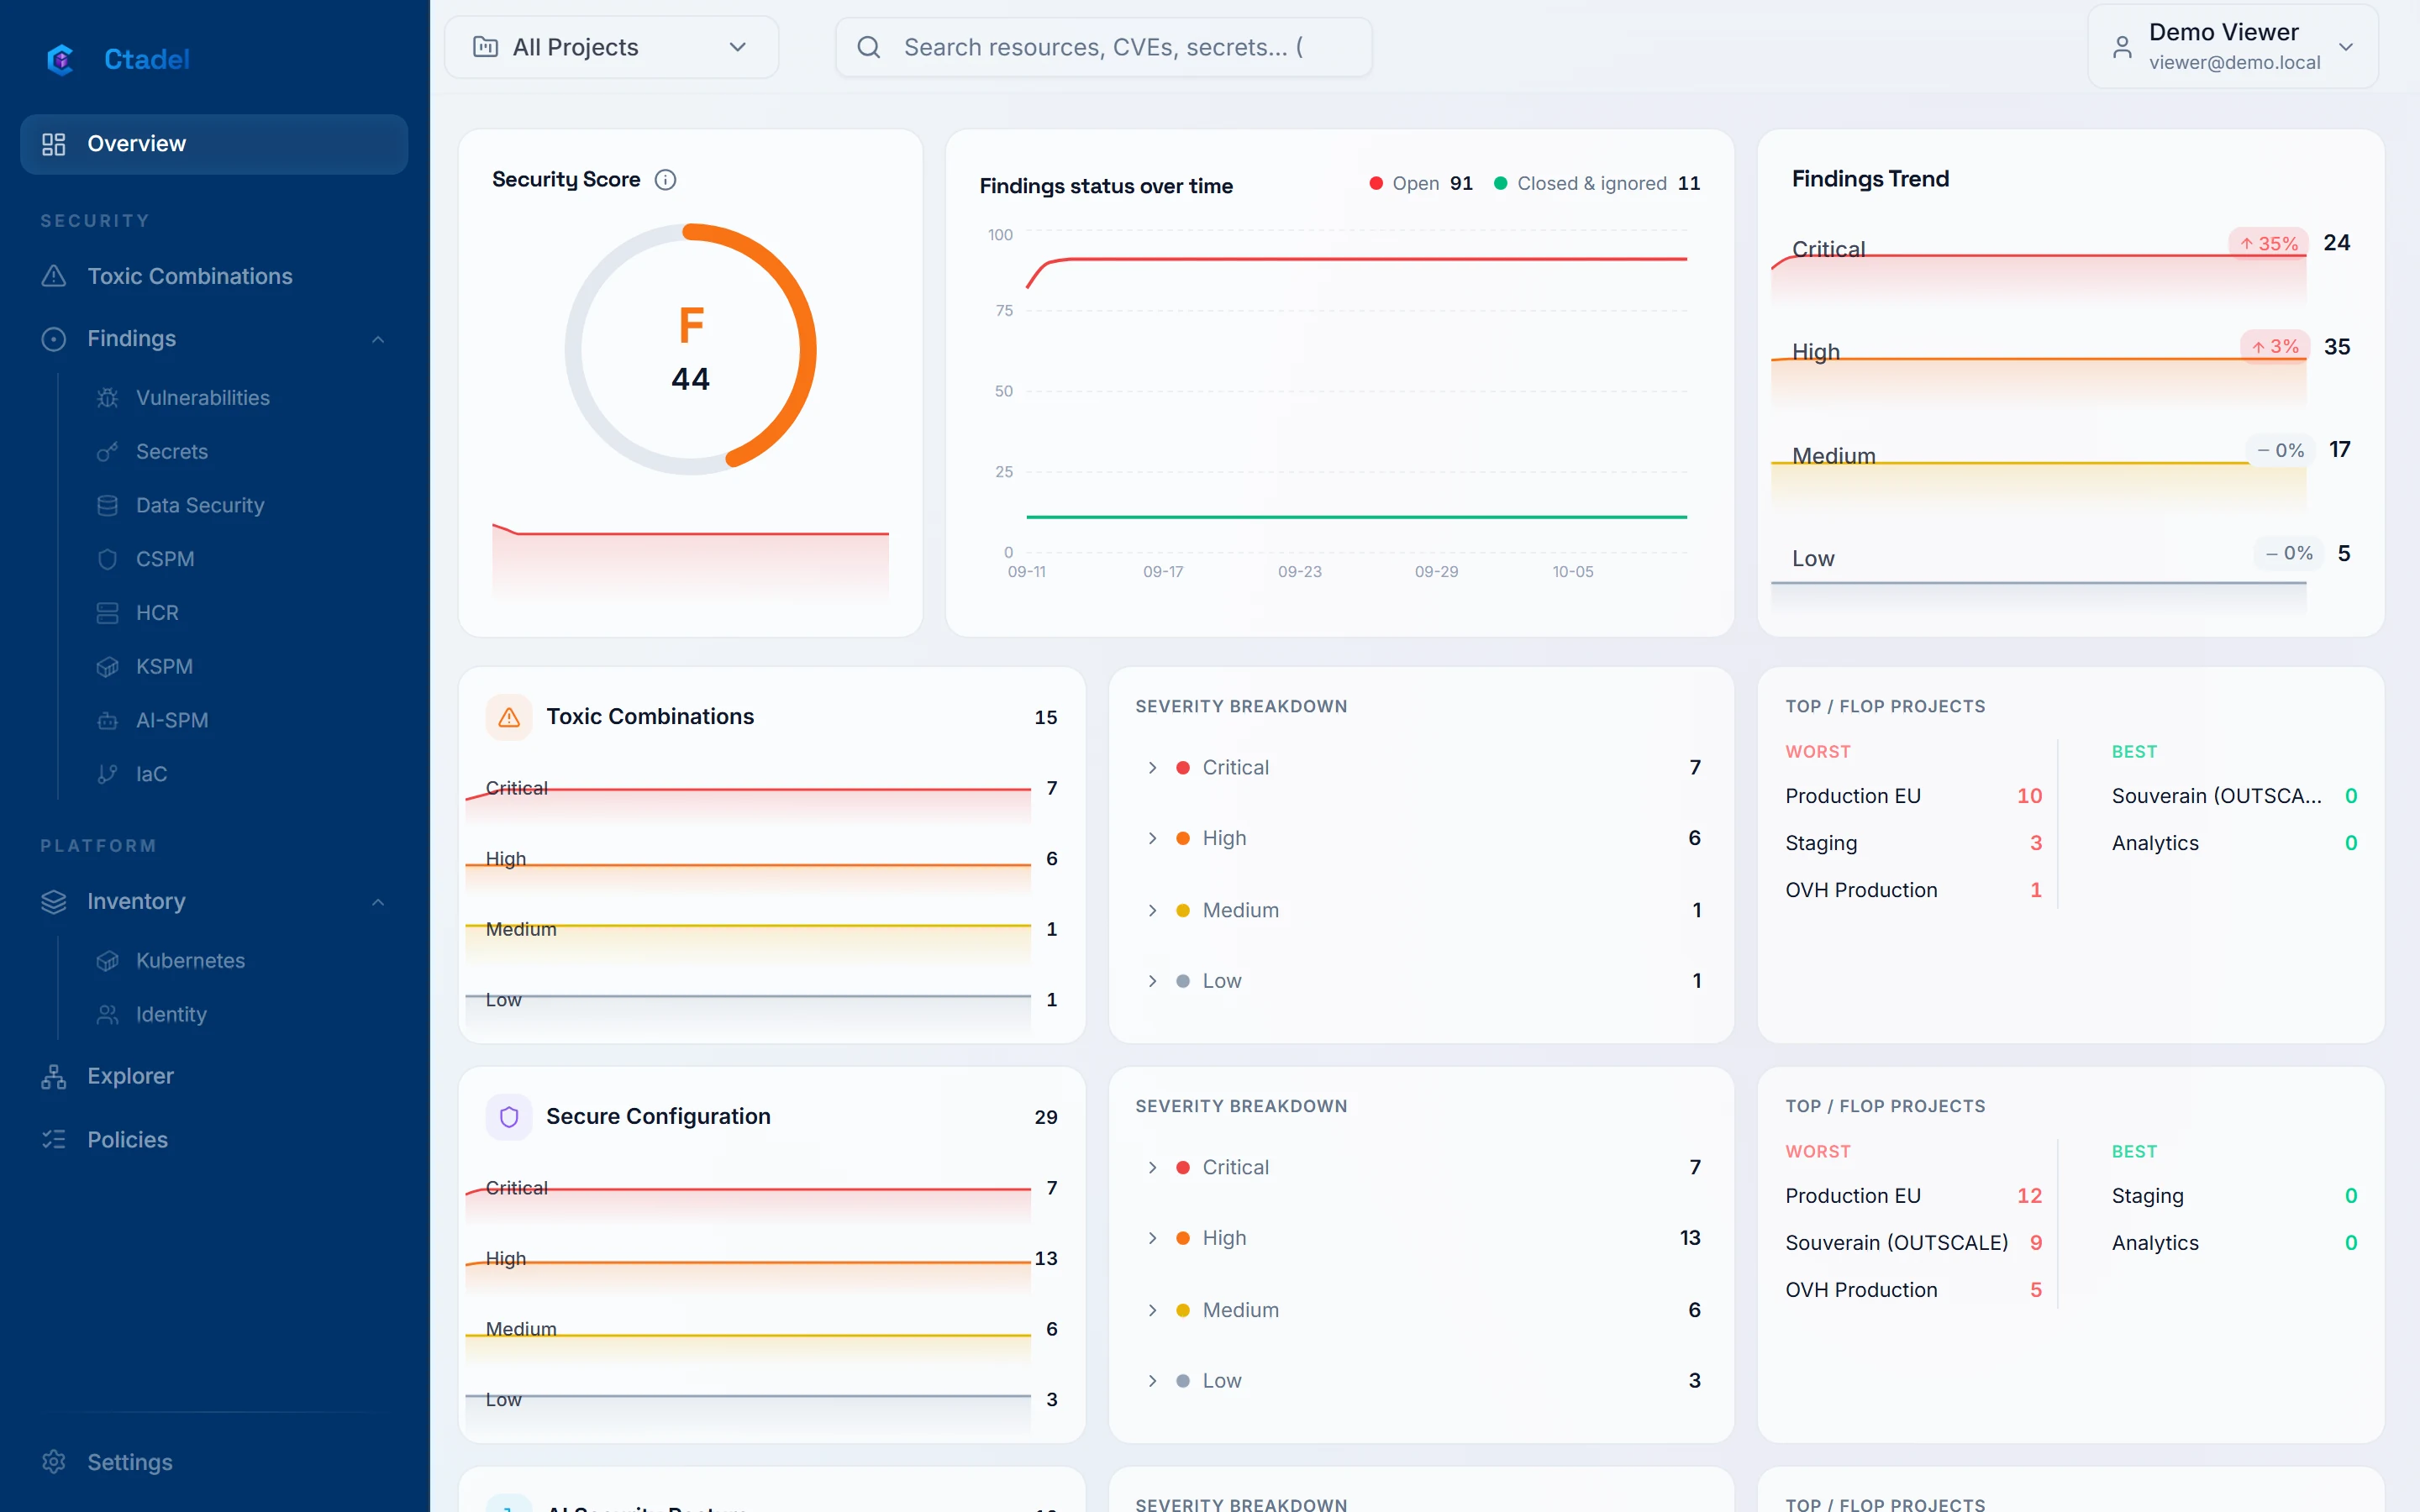
A SOC 2 report requires proving that security controls work over time. Ctadel continuously checks the configuration, access and vulnerabilities of your clouds, and cites the criterion on every finding.
Rules carry the reference of the SOC 2 criterion covered, in the security, availability and confidentiality categories: logical access, encryption, monitoring, change and vulnerability management.
Criterion cited on every finding
Day-by-day score and findings history, for the observation period
Audit log of actions in the application, kept one year
Evidence for the auditor
CSV export of findings with their references, dashboard history, audit log, notifications and tickets that trace the handling of each finding.
What Ctadel does not do
Every rule in the catalogue cites the controls of the frameworks it covers. Those references appear in the detail panel of each finding and export with them. Reports per framework are under internal validation; Ctadel claims no certification for itself.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.