Skip to content
Compliance

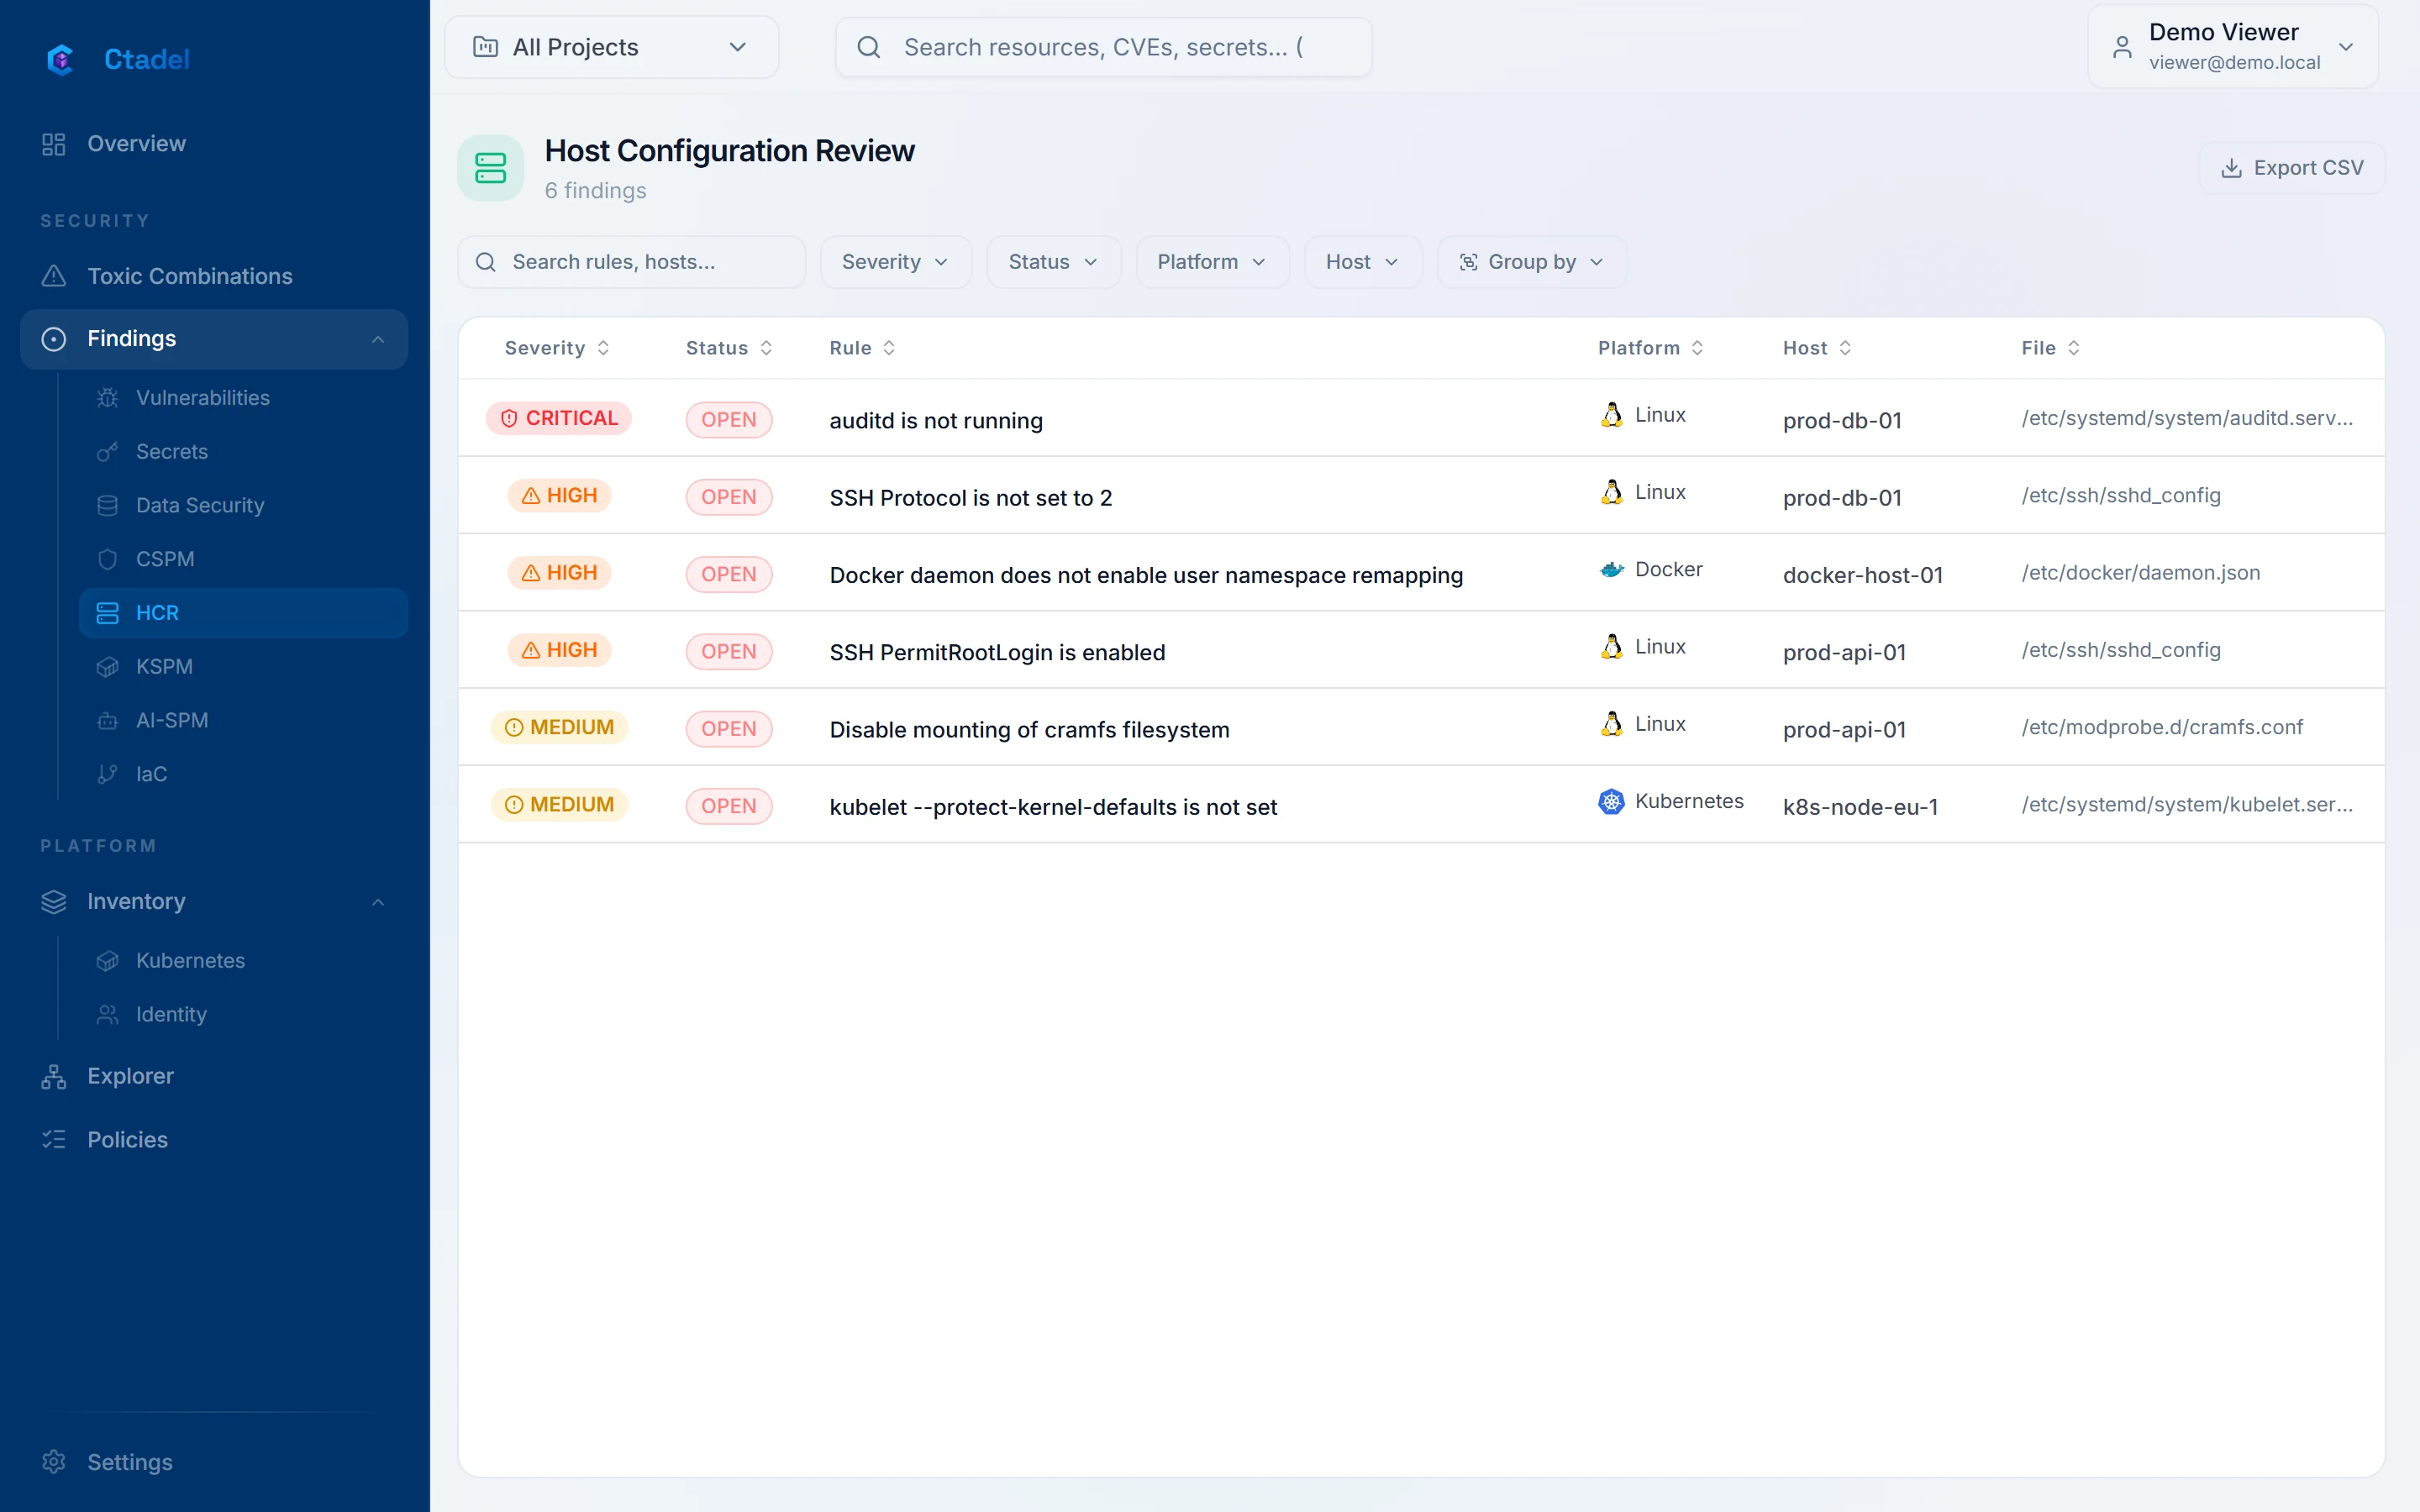
CIS Benchmarks, from the cloud account to the operating system

The CIS Benchmarks describe a hardened configuration, control by control. Ctadel applies them to AWS and Azure accounts, to Linux and Windows hosts read from a disk copy, and to Kubernetes clusters.

CIS Benchmarks, from the cloud account to the operating system

What Ctadel checks

CIS AWS Foundations and CIS Microsoft Azure Foundations on account configuration; CIS Linux and Windows benchmarks on hosts, checked without an agent on a disk snapshot; Pod Security Standards on Kubernetes workloads.

  • CIS recommendation cited on every finding
  • Hosts checked without an agent, audit and rollback commands in the Remediation tab
  • Controls not measurable on a disk copy reported as such

What Ctadel does not do

Every rule in the catalogue cites the controls of the frameworks it covers. Those references appear in the detail panel of each finding and export with them. Reports per framework are under internal validation; Ctadel claims no certification for itself.

On a disk copy, the state of running services is not observable: those controls are reported as not evaluated, not as compliant.

See it on your accounts

The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.