What happens without a tool
The records of processing say where the data should be. Reality is in backup buckets, shared snapshots and test exports. A compromised key stays valid for months.

Backups in a forgotten bucket, an API key in a function variable, and no certainty about what they contain.
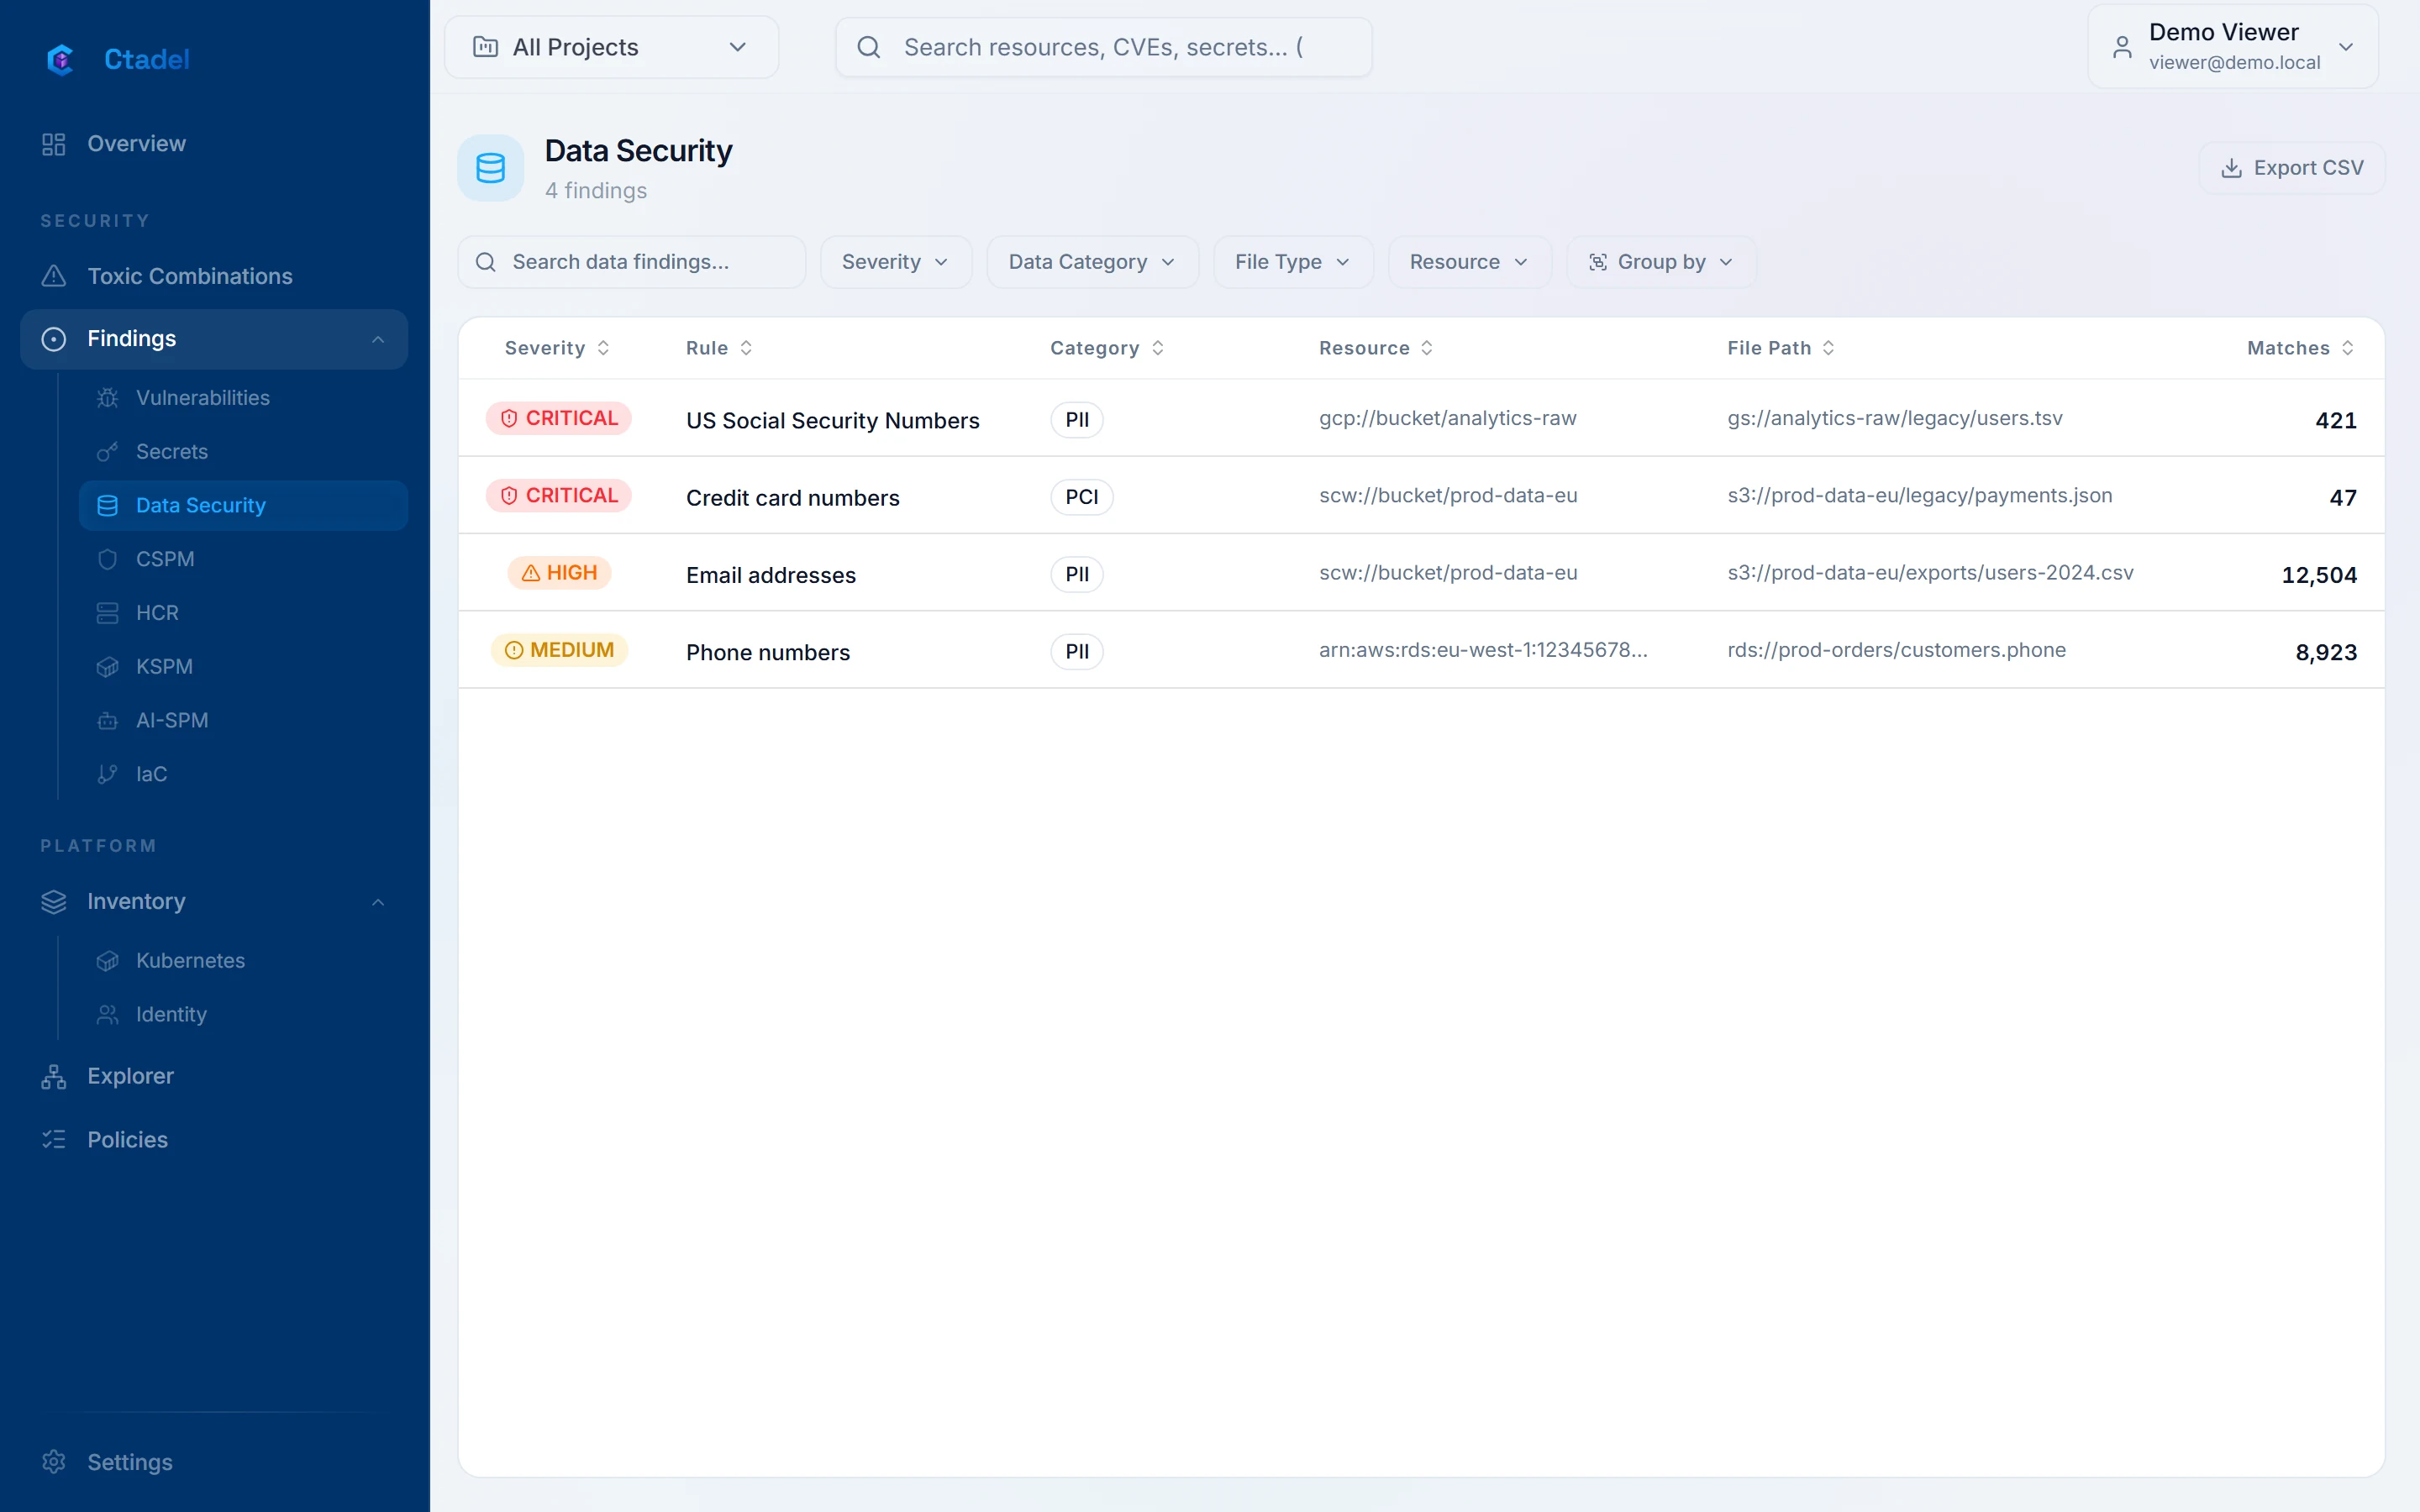
The records of processing say where the data should be. Reality is in backup buckets, shared snapshots and test exports. A compromised key stays valid for months.
The Data scanner samples buckets and reads databases on a temporary copy inside your account, then classifies what it finds by category, masked excerpts. The Secrets scanner finds API keys, tokens, passwords and private keys in buckets, disks, functions and repositories, and checks whether they still work. Every piece of data found joins the attack path graph.
Grant bucket content read permissions and, if you wish, database copy permissions. The Data scanner runs on the next scan; results are on the Data page.
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.