The misconfiguration is discovered in production, by a scanner or by an incident. Fixing it then requires a code change, a review and a deployment, for a problem that would have fitted in one comment line on the pull request.
What Ctadel does
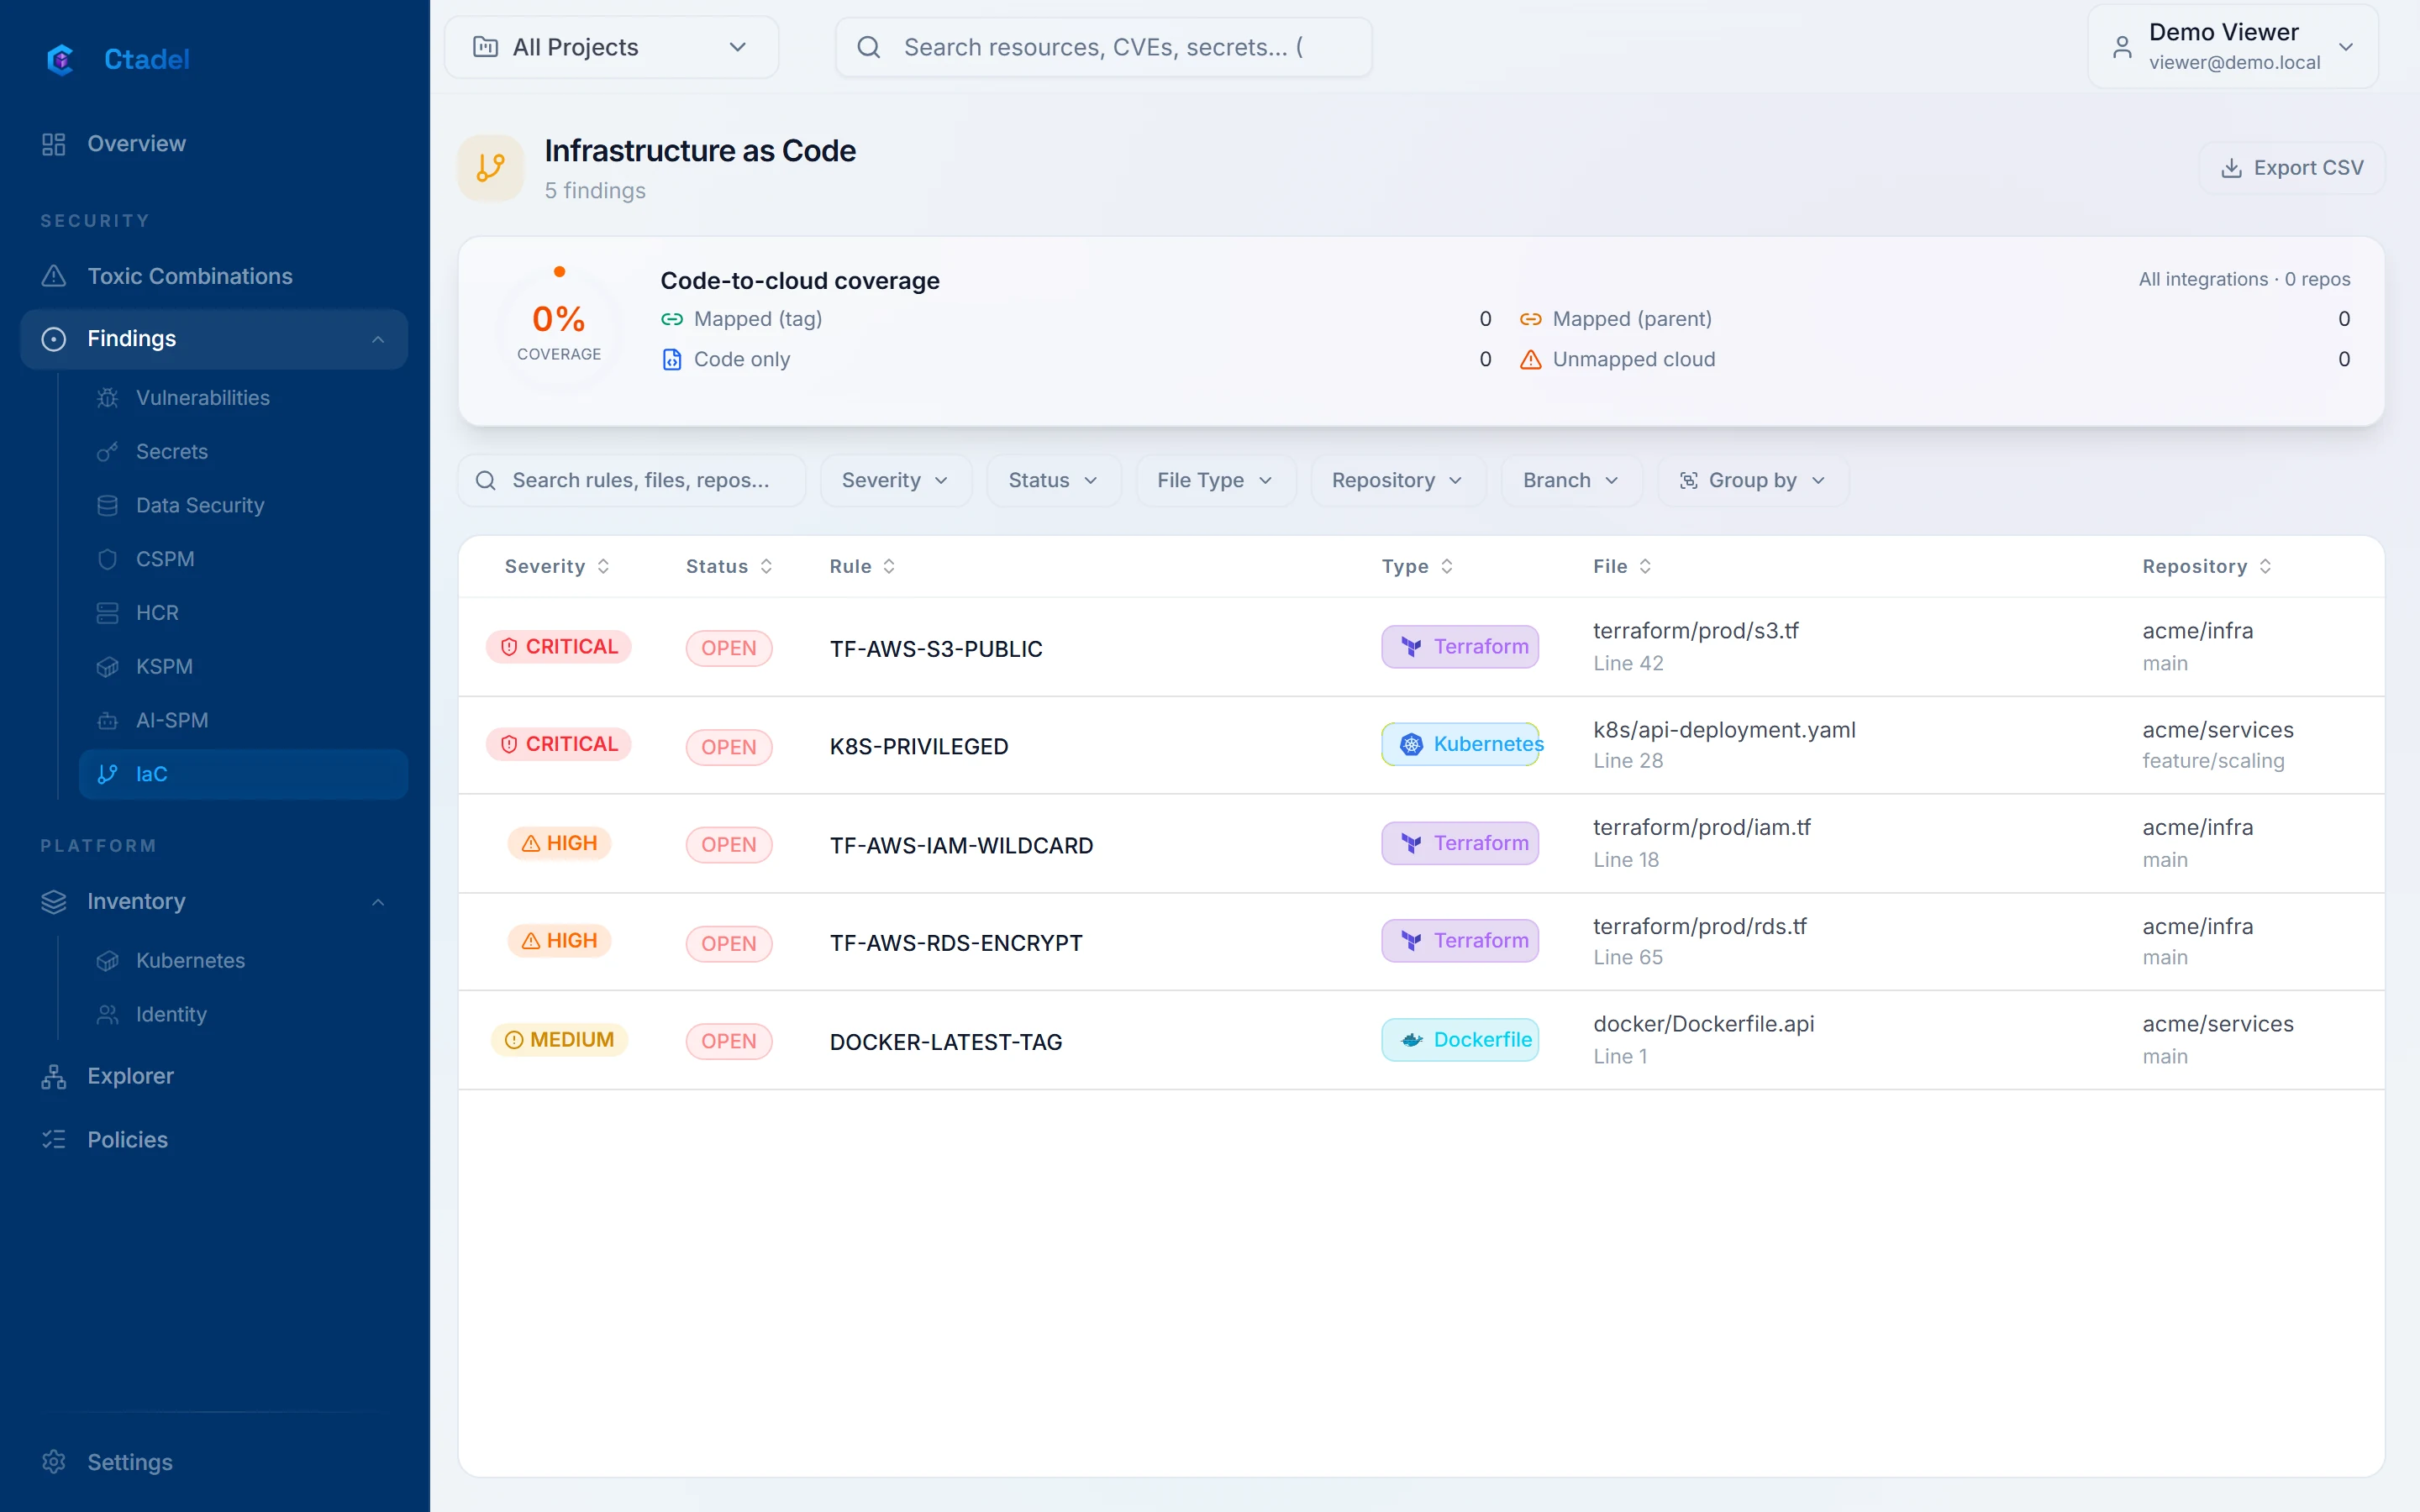
GitHub and GitLab repositories are analysed on every push and pull request: Terraform for the six clouds, Kubernetes manifests, Dockerfiles. A comment and a status are posted on the GitHub pull request. For paired rules, drift between the code and what runs is reported, and a cloud finding points to its Terraform line. The Mason assistant prepares the file change, which you review.
Comment and status on the pull request
Code / deployed drift for paired rules
Fix proposed by the Mason, reviewed by you
How to start
Install the GitHub app or connect GitLab through OAuth from the settings, choose the repositories. A repository’s .ctadel.yaml file attaches it to a project.
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.