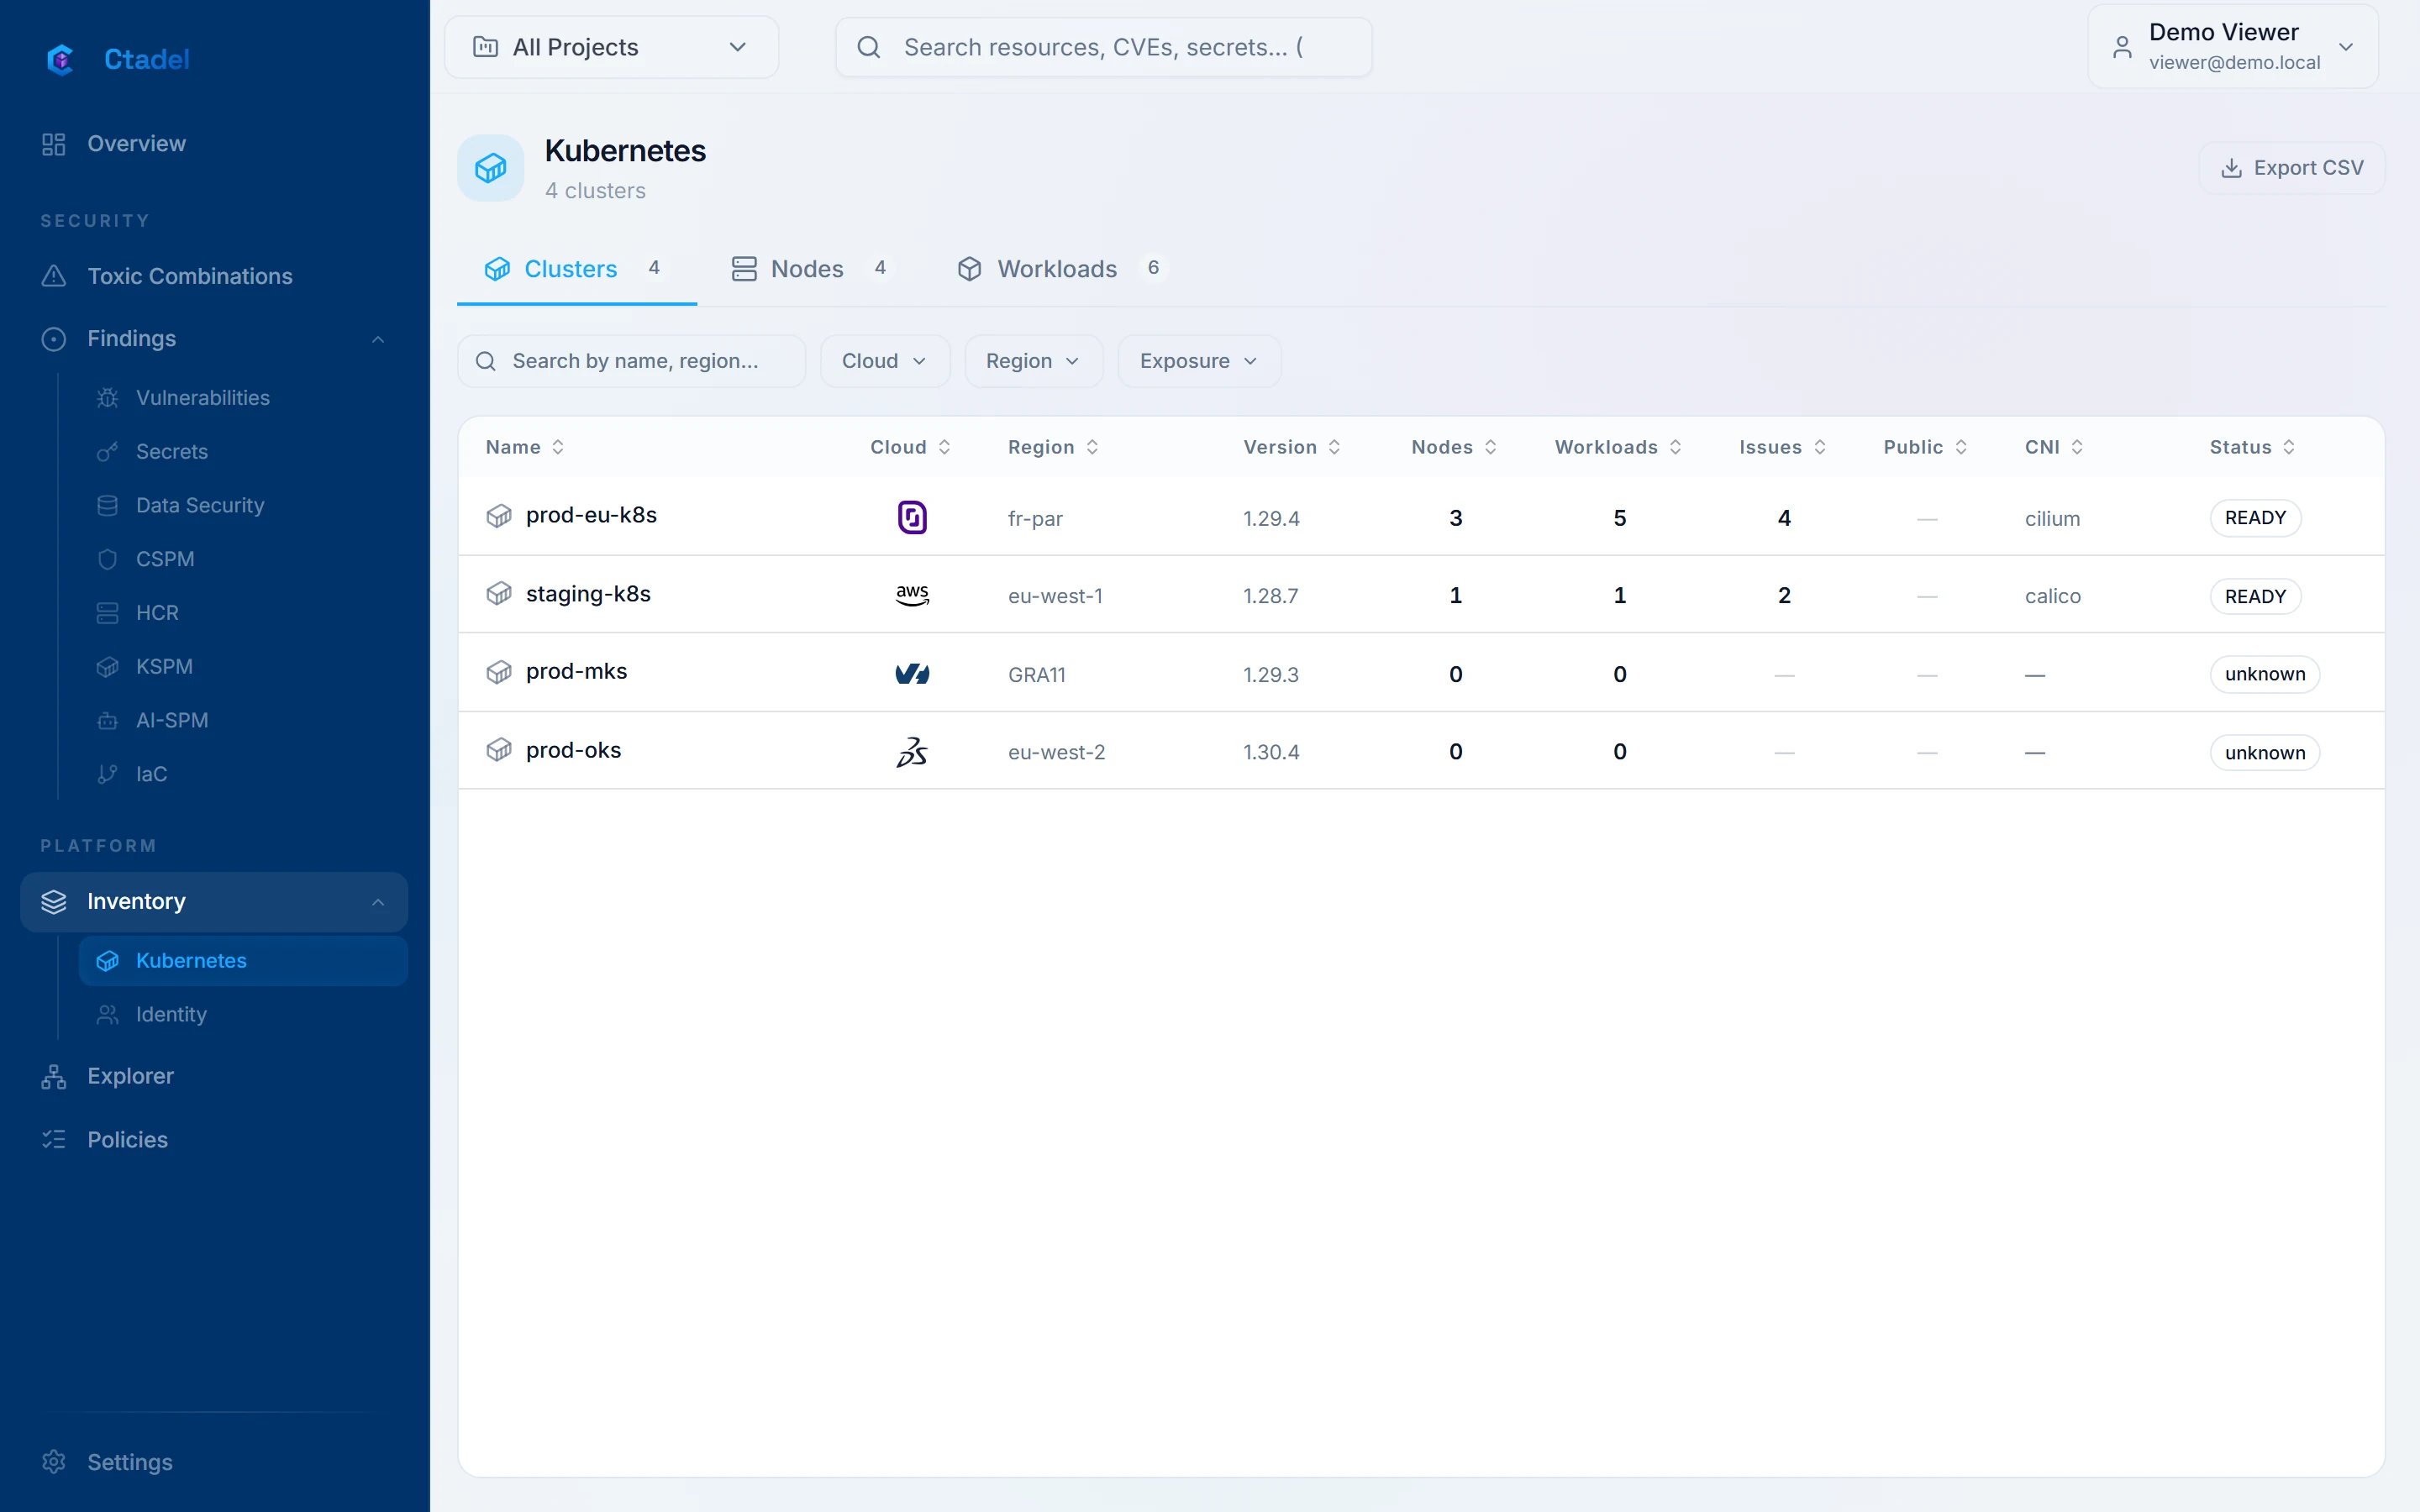
The cluster is discovered during the subscription inventory. Ctadel obtains the cluster admin kubeconfig through the Azure API; if you prefer to limit access, provide a read-only kubeconfig in the application: it takes precedence over the cloud credentials.
What is read
Workloads, service accounts, RBAC, network policies, secrets and configmaps, nodes and images. Running images are analysed for vulnerabilities. The cluster enters the same graph as the cloud account hosting it: a privileged pod on a node reachable from the internet becomes a link of an attack path.
Privileged container or container running as root
API server exposed without address restriction
Service account with a cluster-admin role
Running image with a known exploited vulnerability
See it on your accounts
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.