What vendors look for
A security questionnaire with every large customer, a SOC 2 to obtain to sell in the United States, a product team deploying several times a day, and an API key lying around somewhere.

Answer your customers’ questionnaires with up-to-date evidence, and block misconfigurations before they reach production.
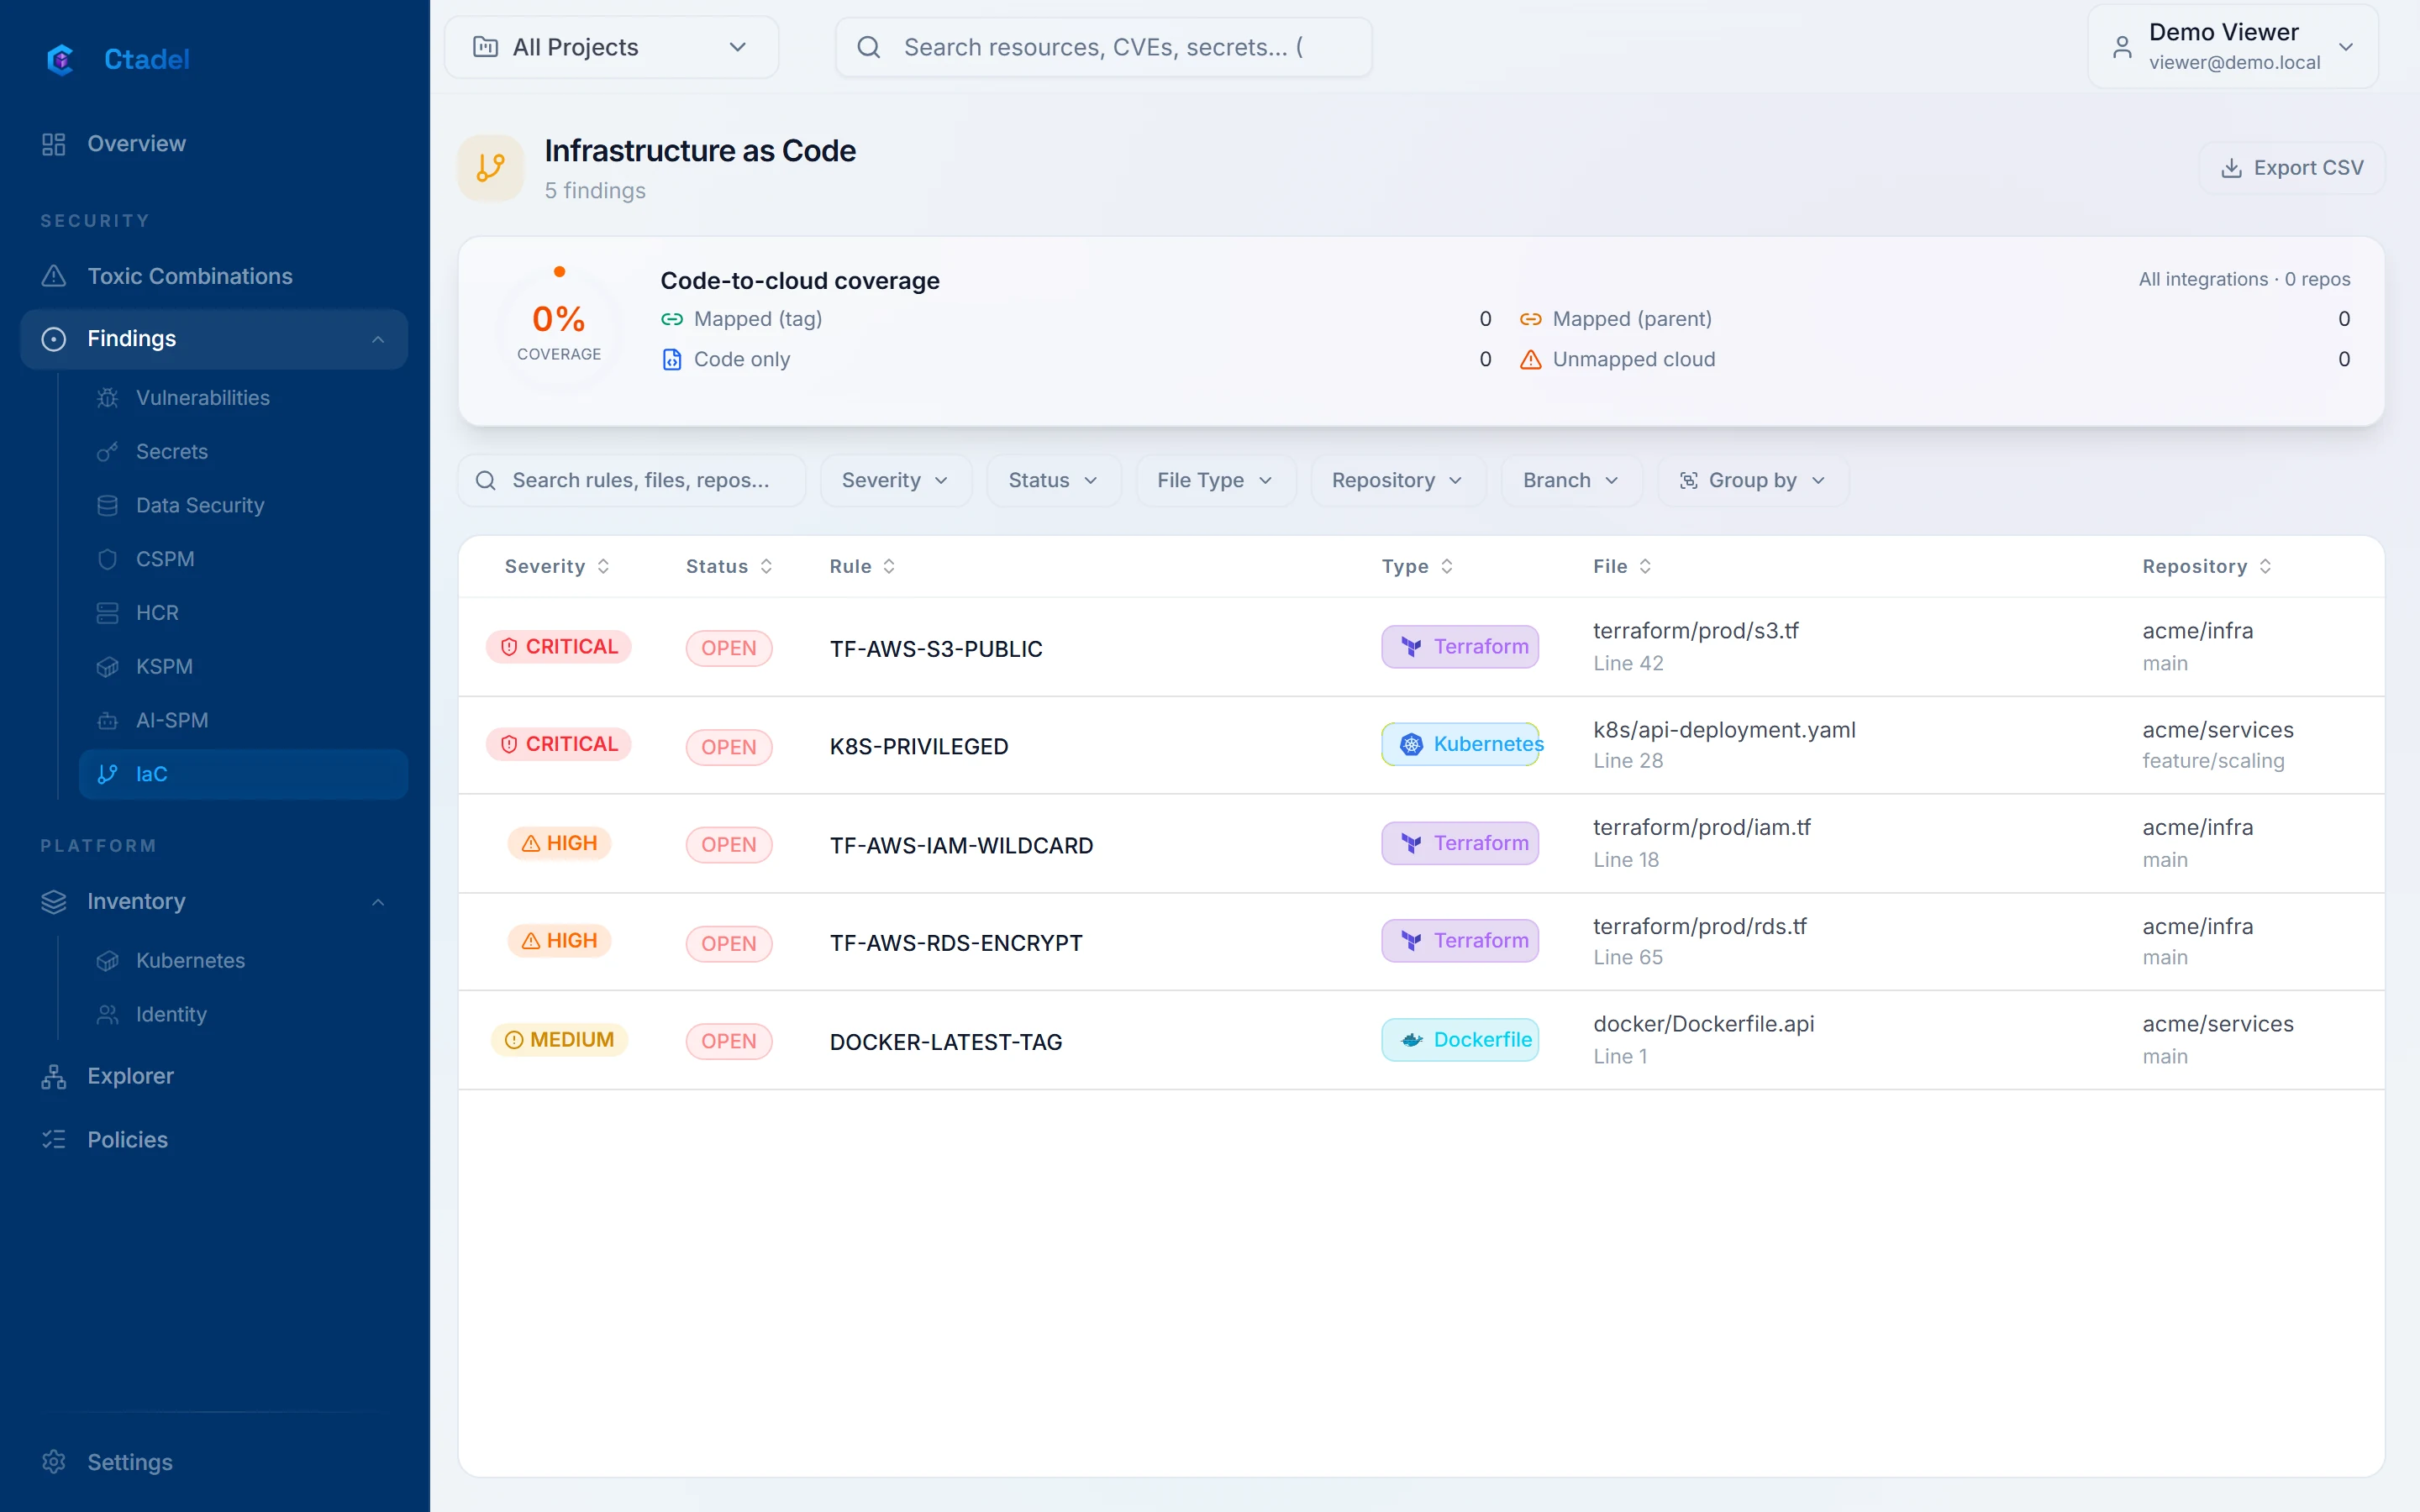
A security questionnaire with every large customer, a SOC 2 to obtain to sell in the United States, a product team deploying several times a day, and an API key lying around somewhere.
GitHub and GitLab pull requests are analysed on every commit: Terraform, Kubernetes, Dockerfiles, secrets, dependencies. Rules cite the SOC 2 criteria and ISO 27001 controls covered. The Secrets scanner finds keys and checks whether they still work. Findings export with their references for questionnaires.
Ctadel does not issue a SOC 2 report; it provides the technical evidence to your auditor.
The online demonstration is open to all, on fictitious data. For an instance on your own accounts, request a demonstration.